
Representative Foreword

After the Code, the Structure Remains

The representative foreword of this blog: security now fails less at finding issues than at absorbing, sustaining, and acting on what has already been found.

This essay frames the entire site first. The posts on technical analysis, method, and governance all start from this same problem statement.

After the Code, the Structure Remains

Detection, Method, Governance

🔥 A Mind That Dissects Systems

🔥 Trust and Culture Beyond Technology

🔥 Code That Fixes, Not Just Runs

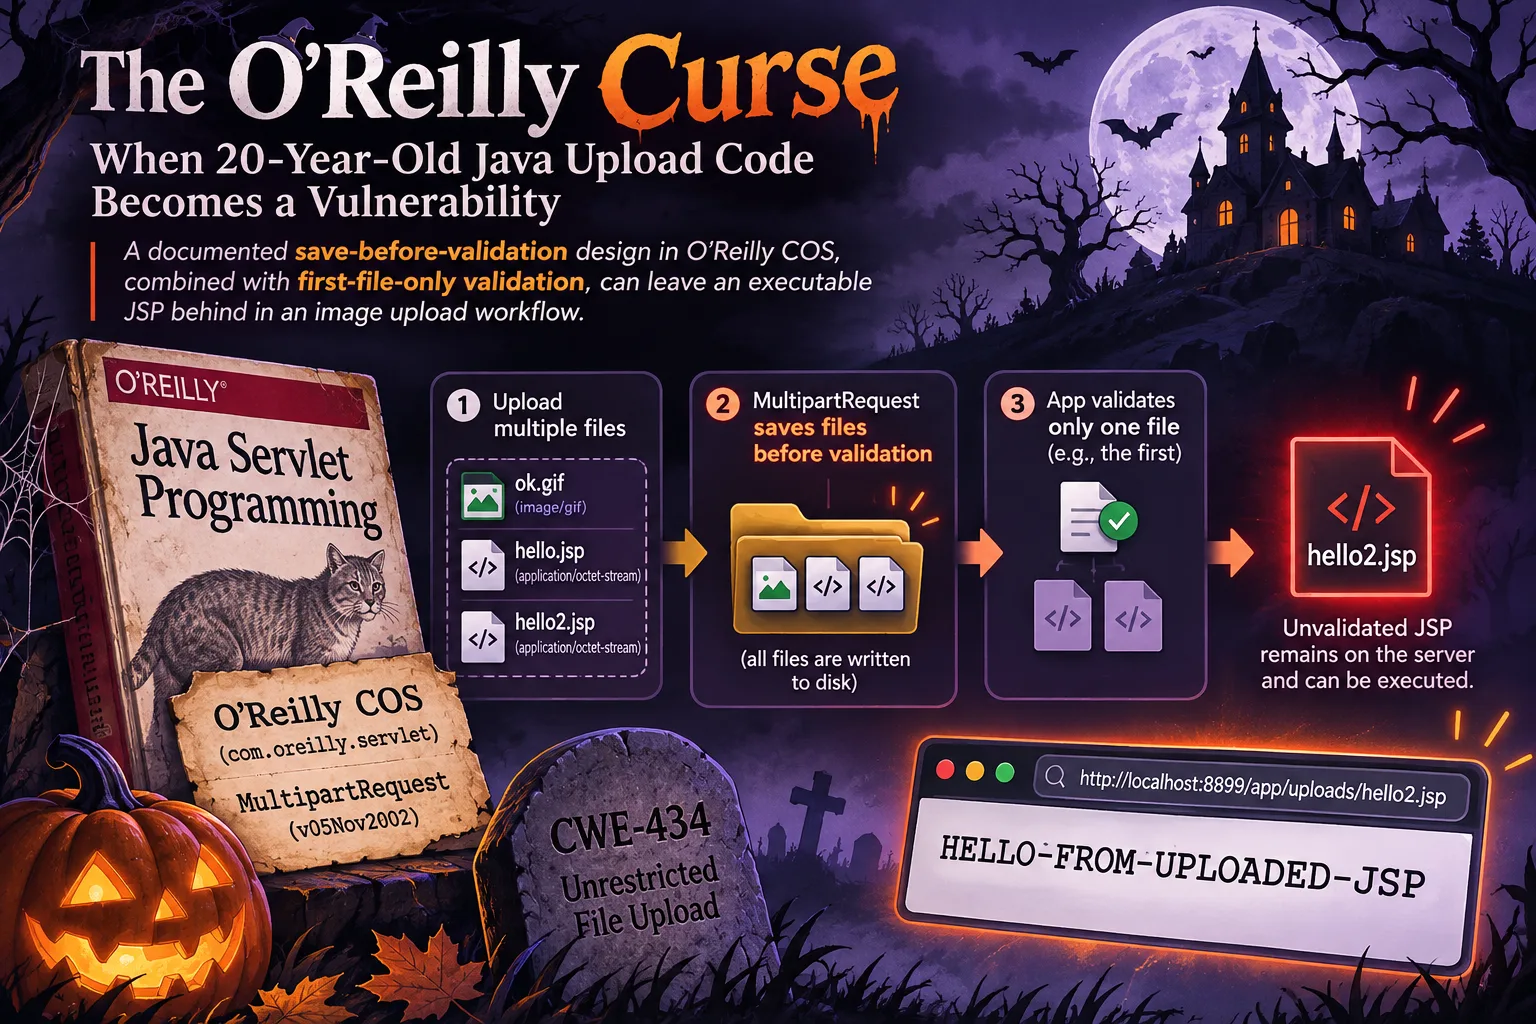
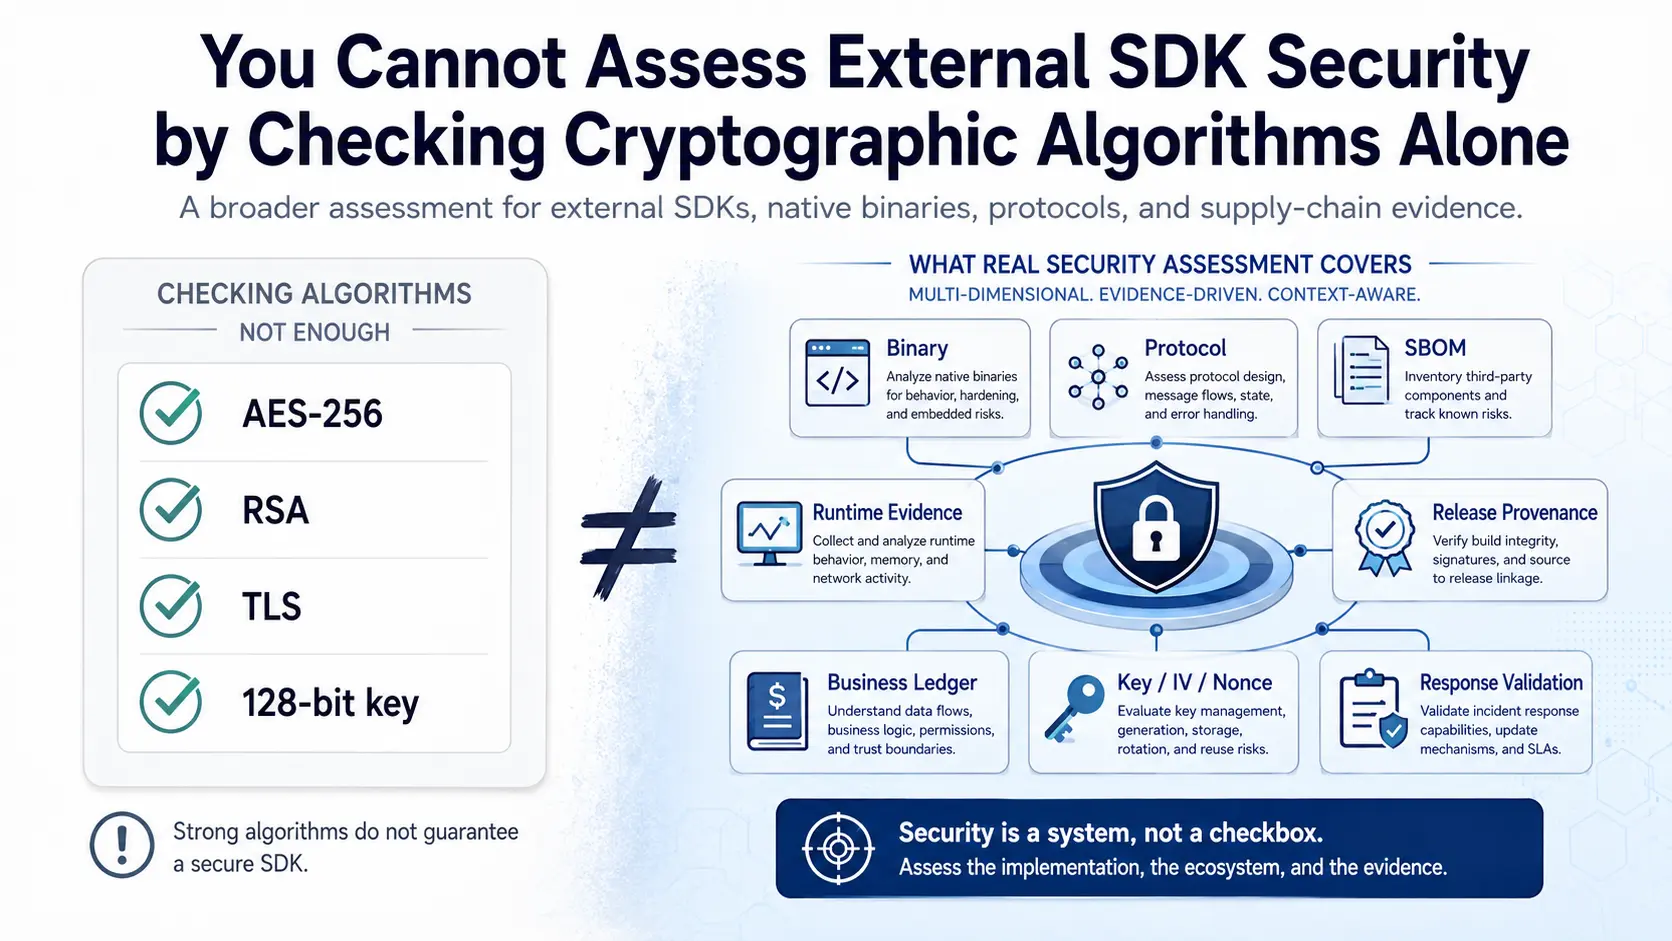
The O'Reilly Curse infographic — how O'Reilly COS MultipartRequest's save-before-validation and first-file-only validation can leave an executable JSP behind in an image-upload flow

The O’Reilly Curse: When 20-Year-Old Java Upload Code Becomes a Vulnerability

A documented save-before-validation design in O’Reilly COS MultipartRequest, combined with first-file-only application validation, can leave an executable JSP behind in an image-upload flow. A CWE-434 case study through code, a reproduction walkthrough, and the proper fix.

November 2, 2026 · 7 min · 1375 words
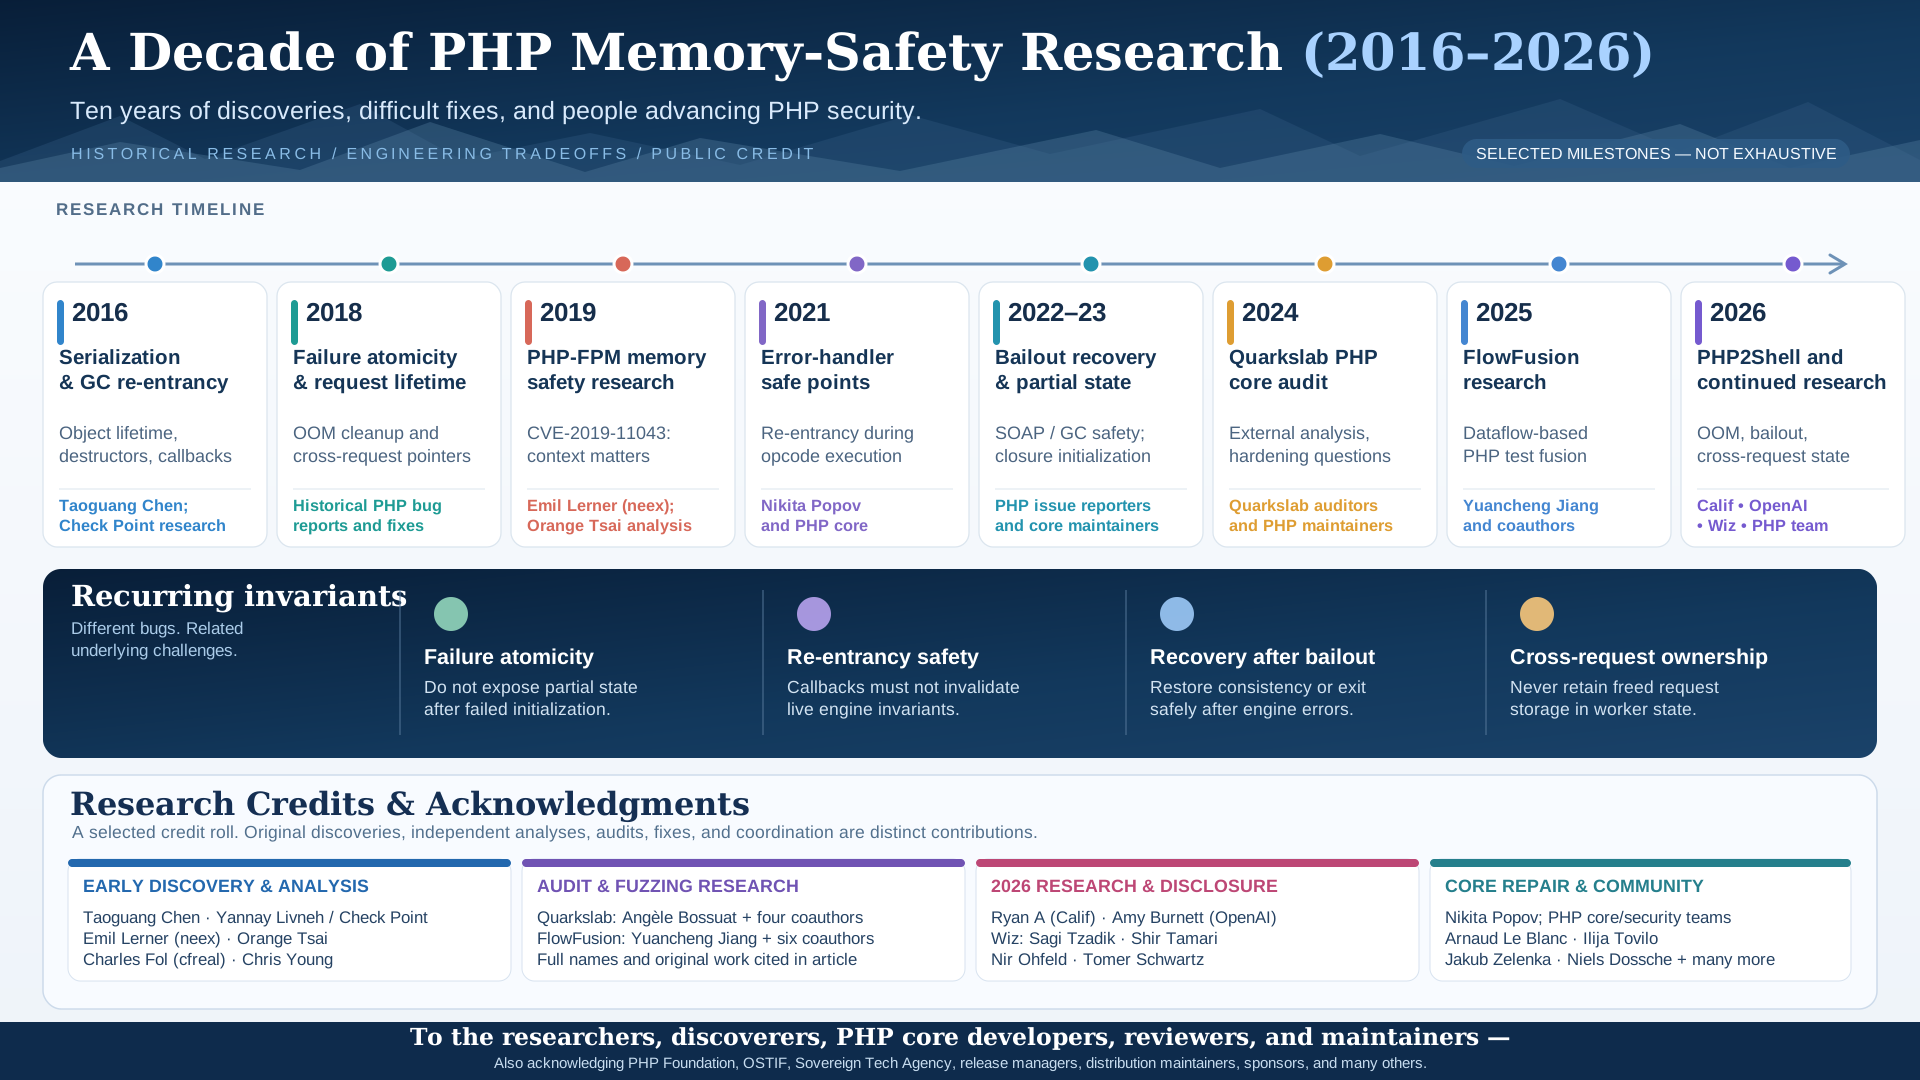
English timeline of PHP memory-safety research 2016–2026, original researchers, contributors, and acknowledgments

A Decade of PHP Memory-Safety Bugs: Why Do the Same Failures Keep Returning?

A technical retrospective on a decade of PHP memory-safety research, crediting original discoverers and maintainers while examining failure atomicity, re-entrancy, bailout recovery, and cross-request ownership.

October 24, 2026 · 7 min · 1474 words

PHP Memory-Safety Research Notes (2016–2026): Discoverers, Root Causes, Fixes and Evidence

A source-based provenance map of PHP memory-safety findings from 2016 to 2026, crediting original researchers and maintainers while separating issue status, reproducibility, exploitability, and patch verification.

October 24, 2026 · 7 min · 1407 words

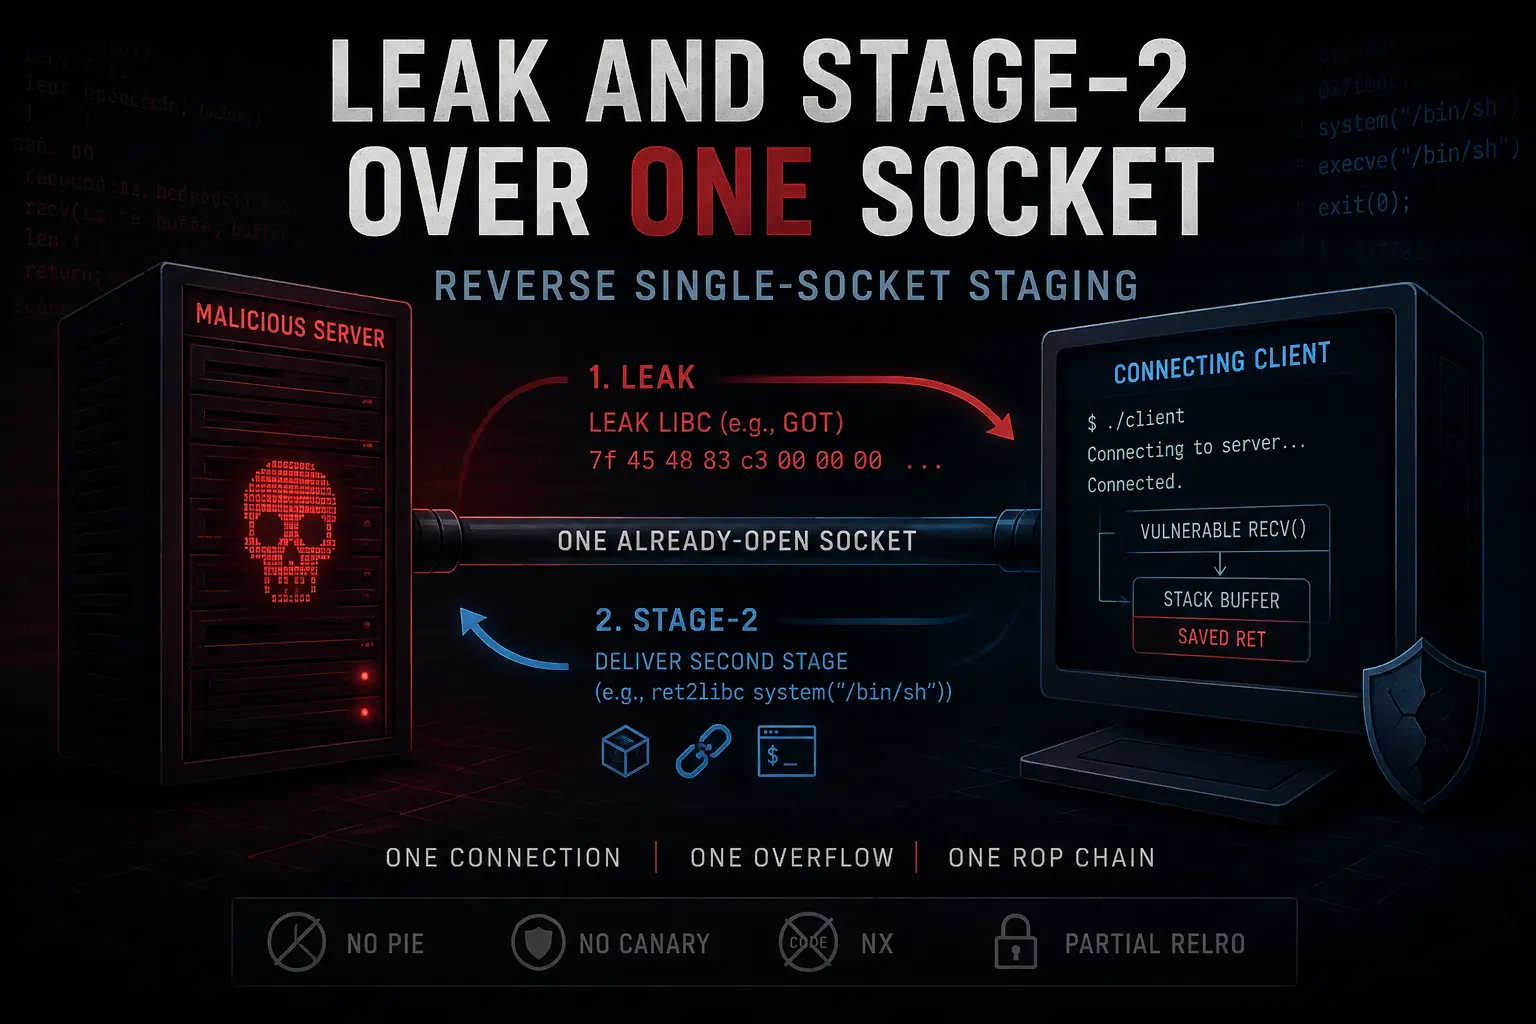
Leak and Stage-2 Over One Socket: Reverse Single-Socket Staging

A malicious server corrupting a client that dials out to it, carrying both the libc leak and the second stage over one already-open socket in a single ROP chain. And why this is not a new pattern but a well-known composition.

August 15, 2026 · 10 min · 1947 words

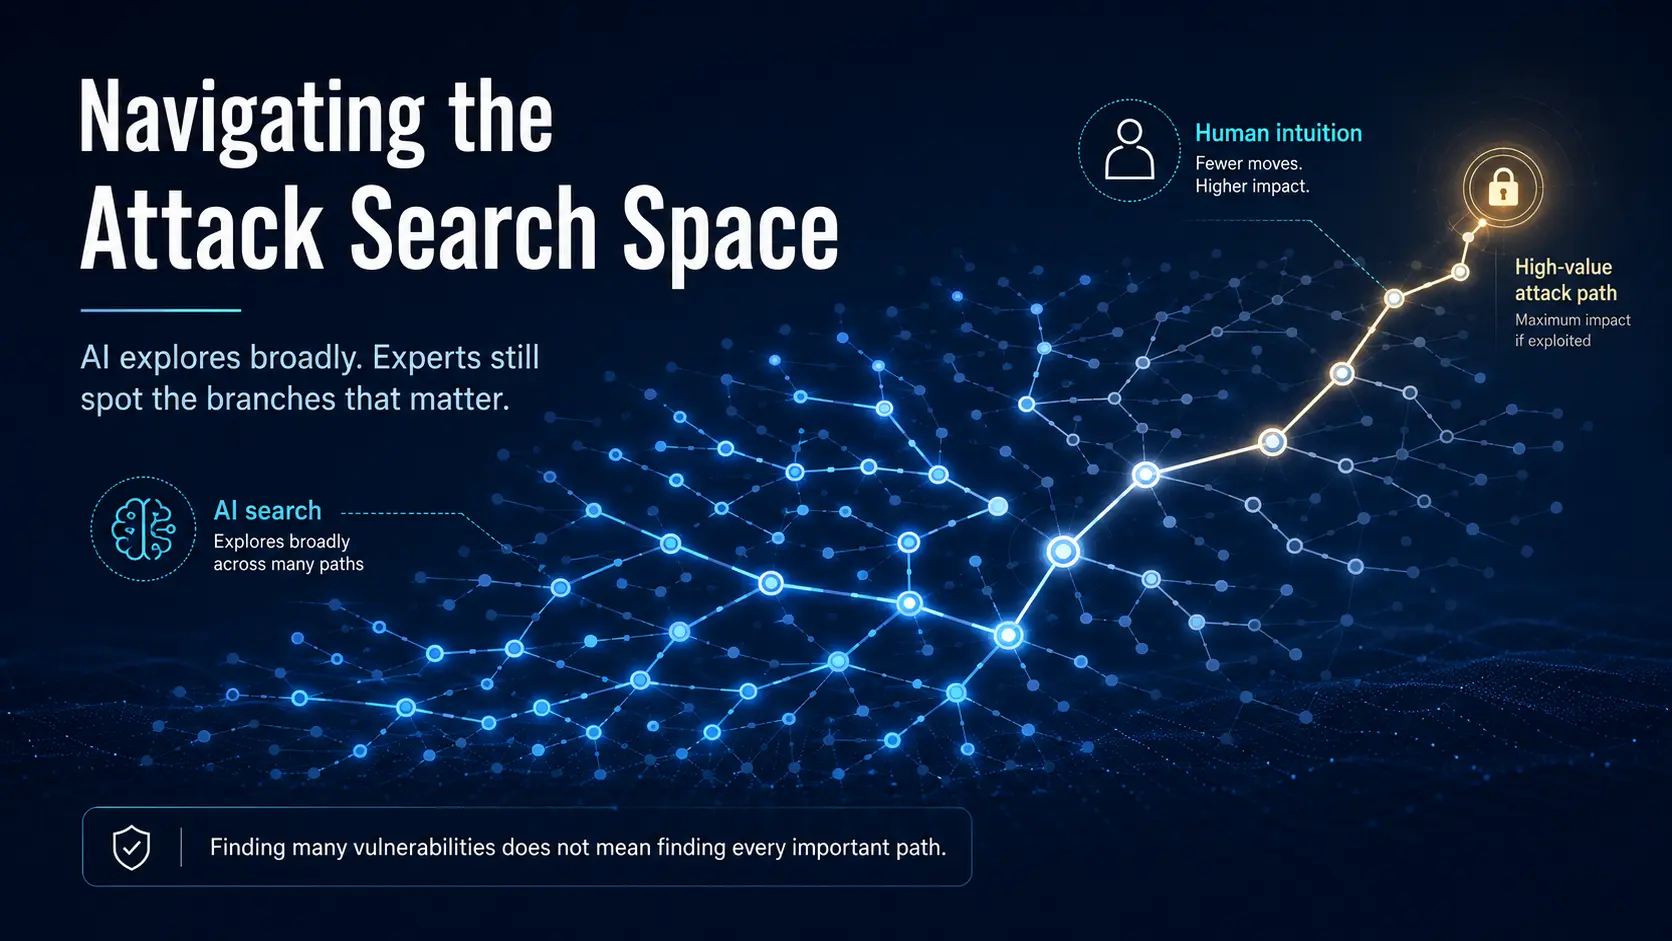
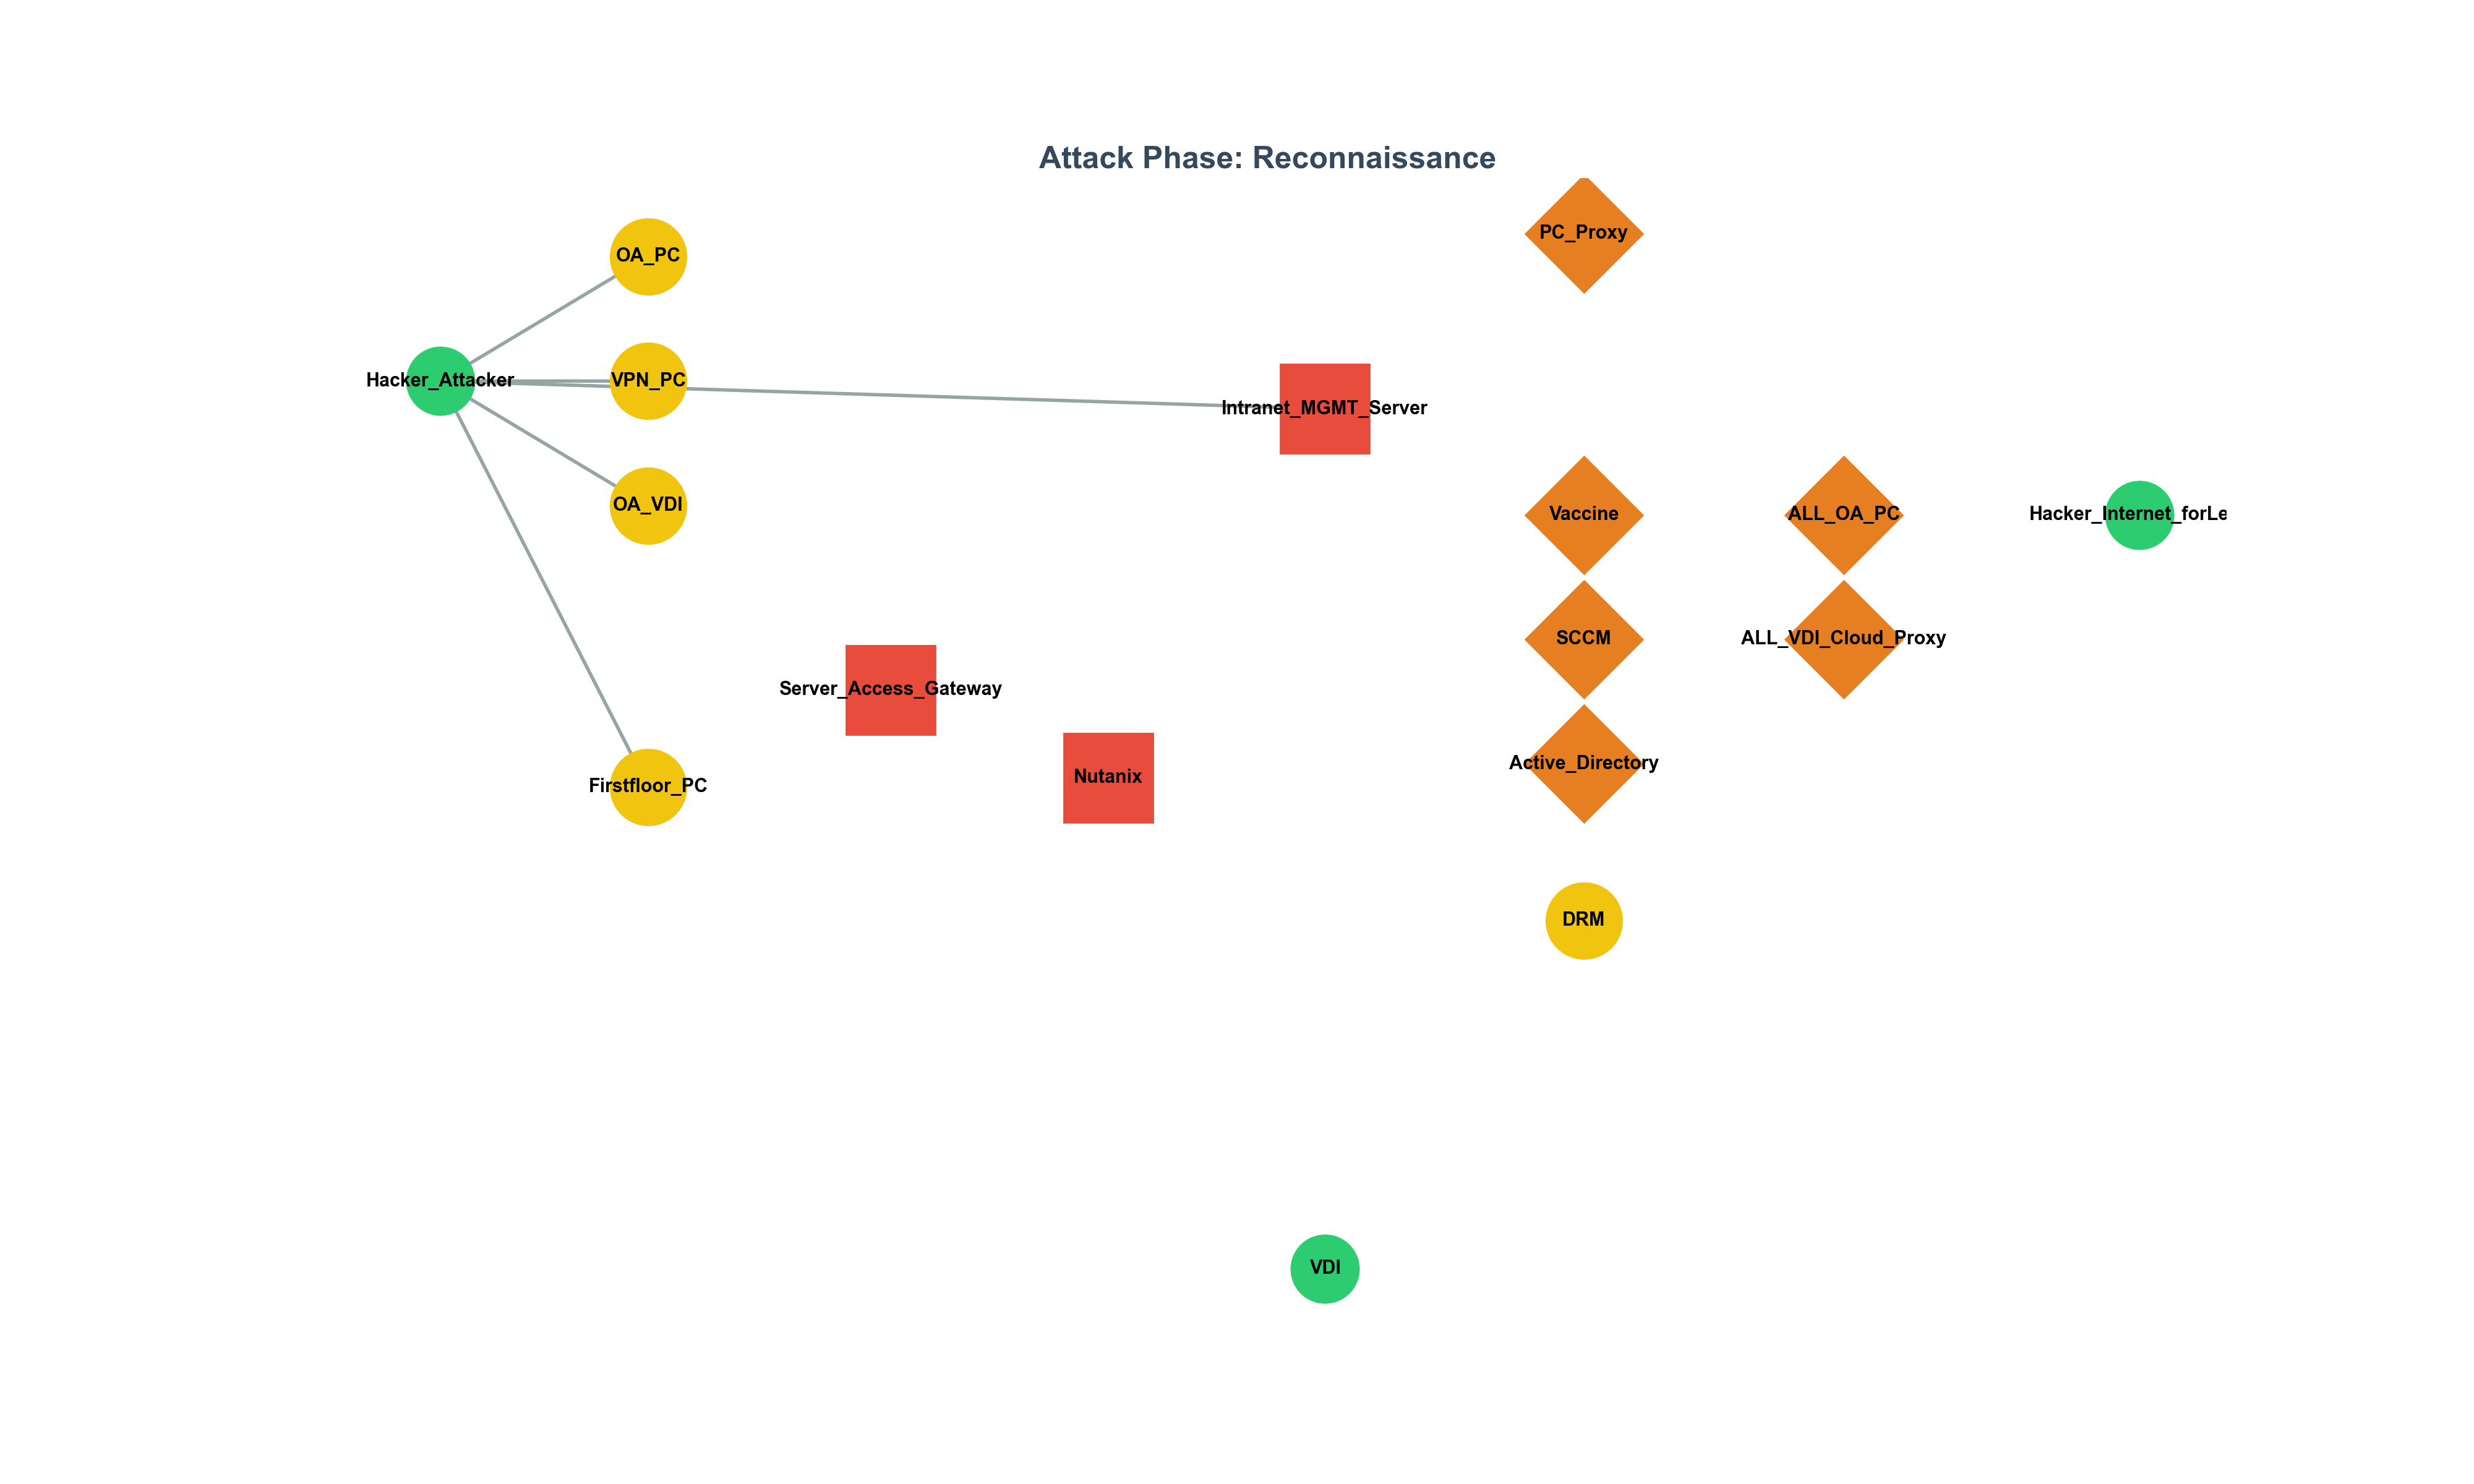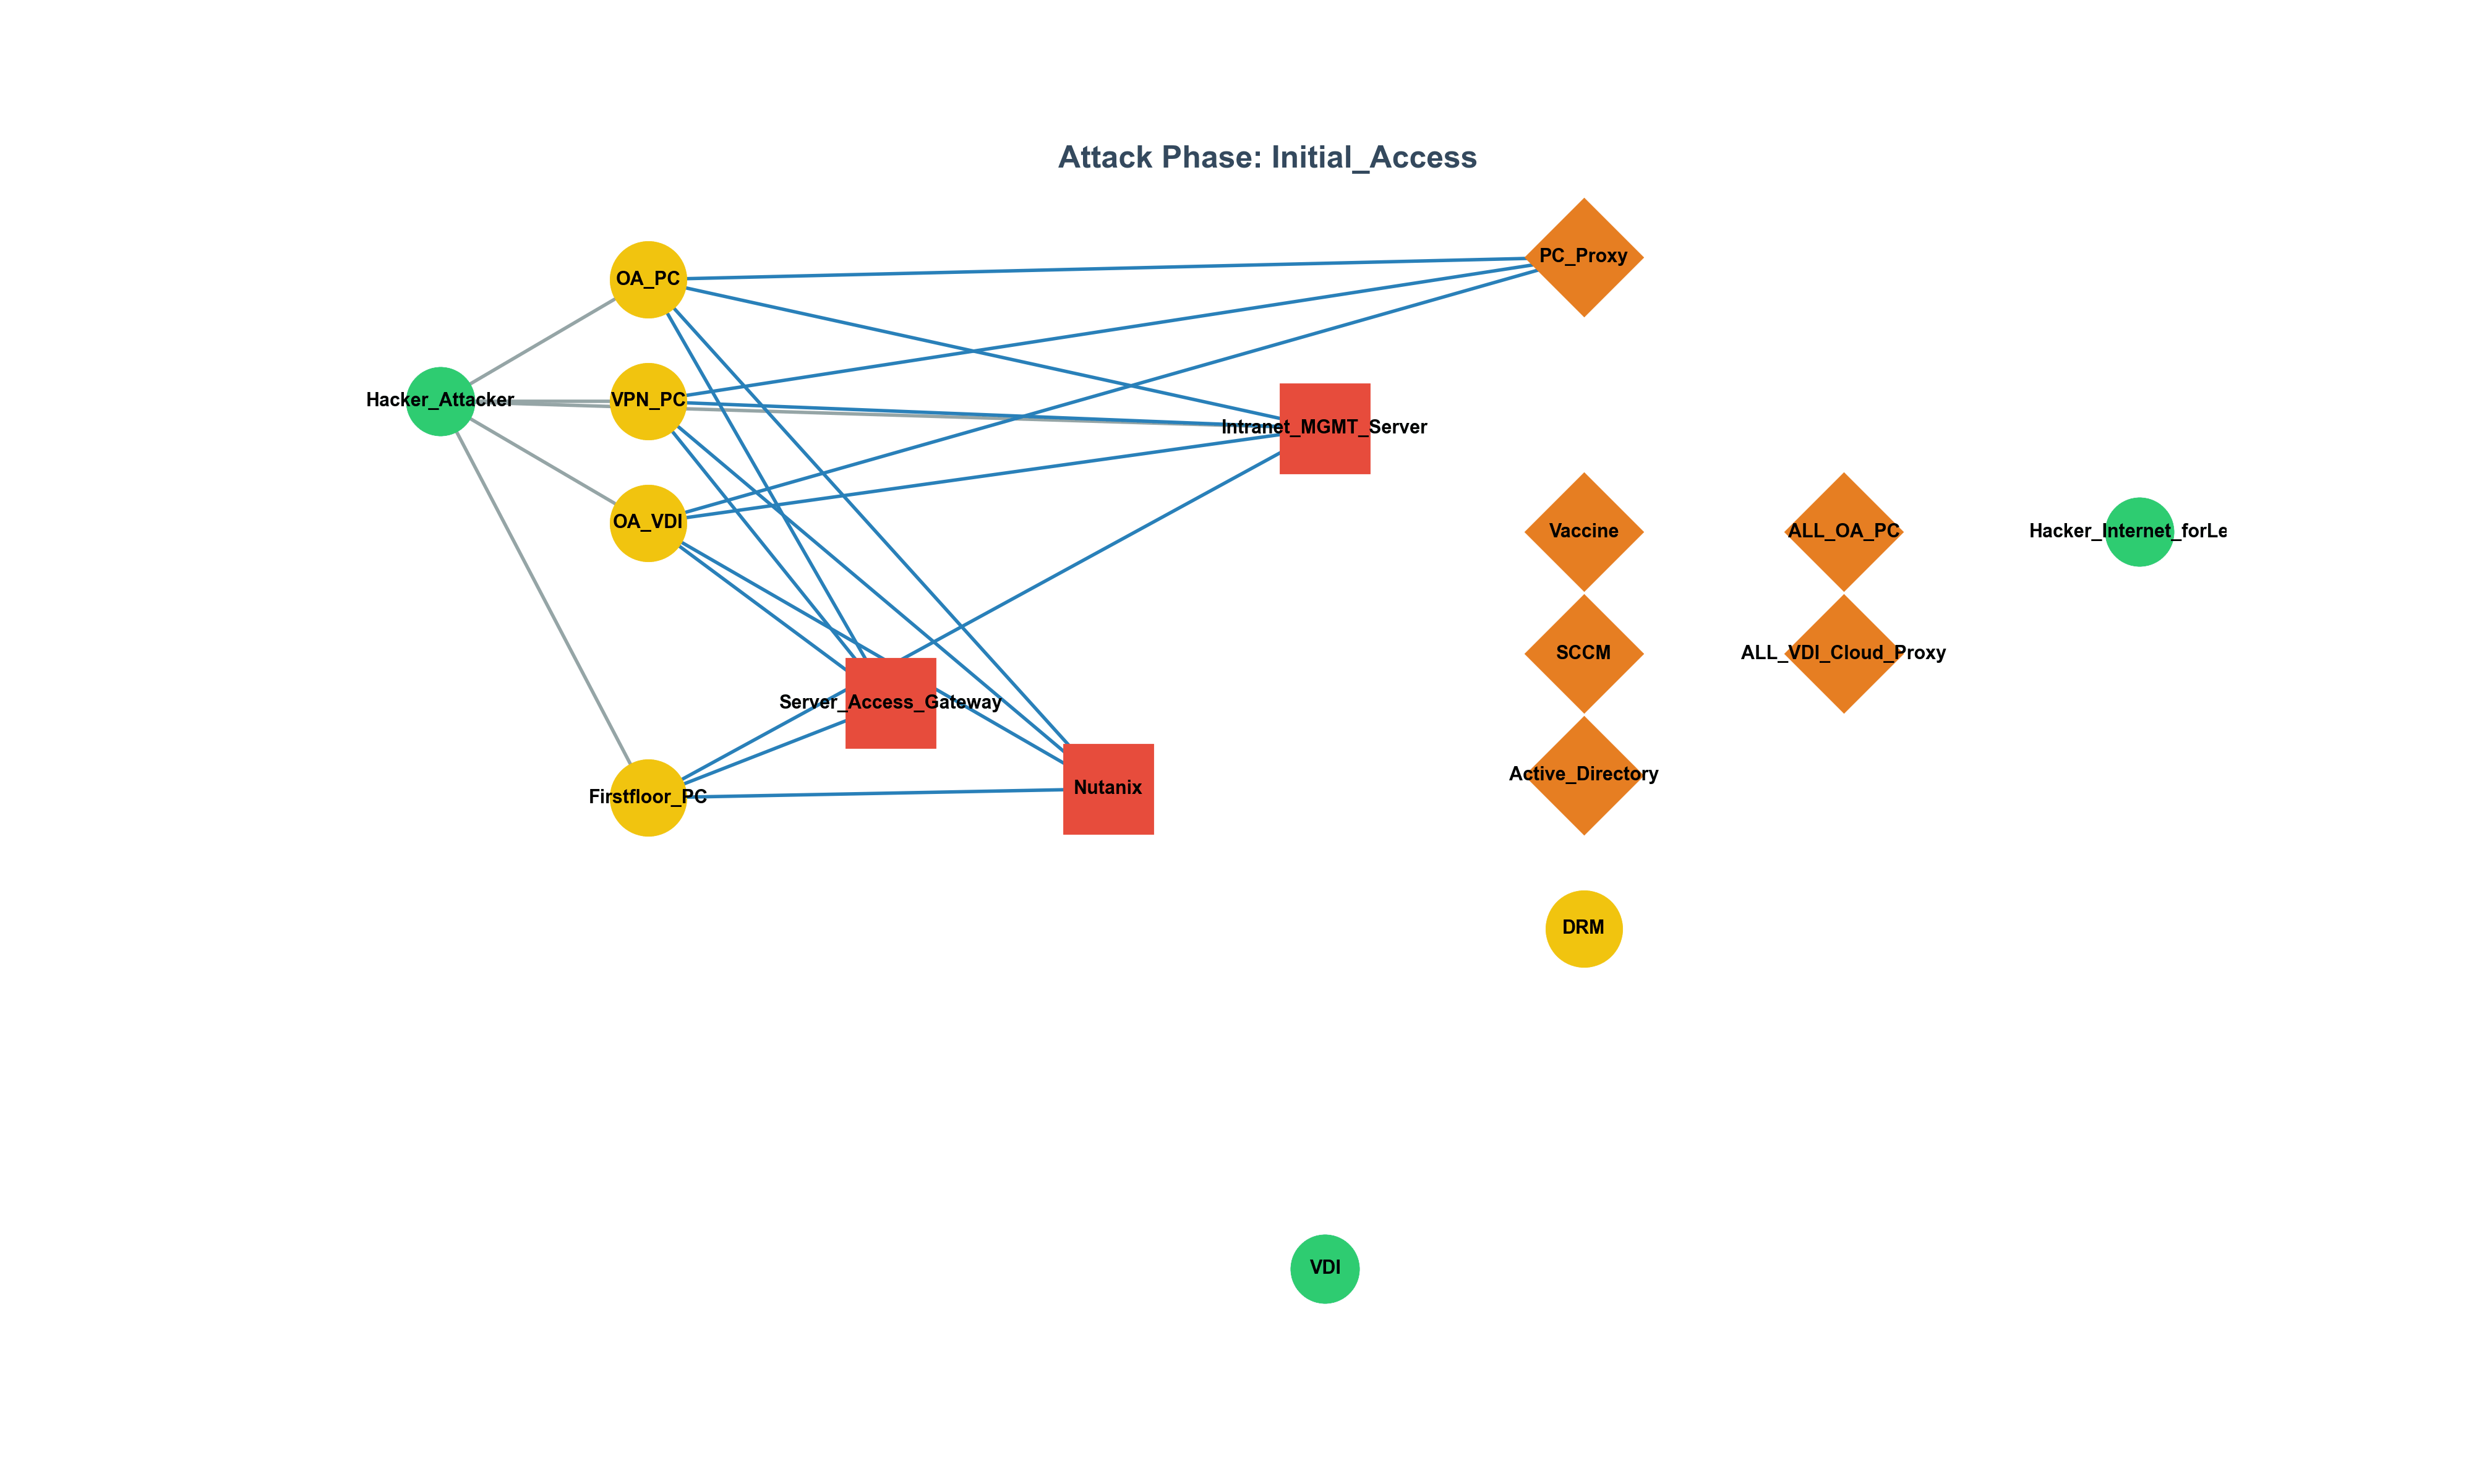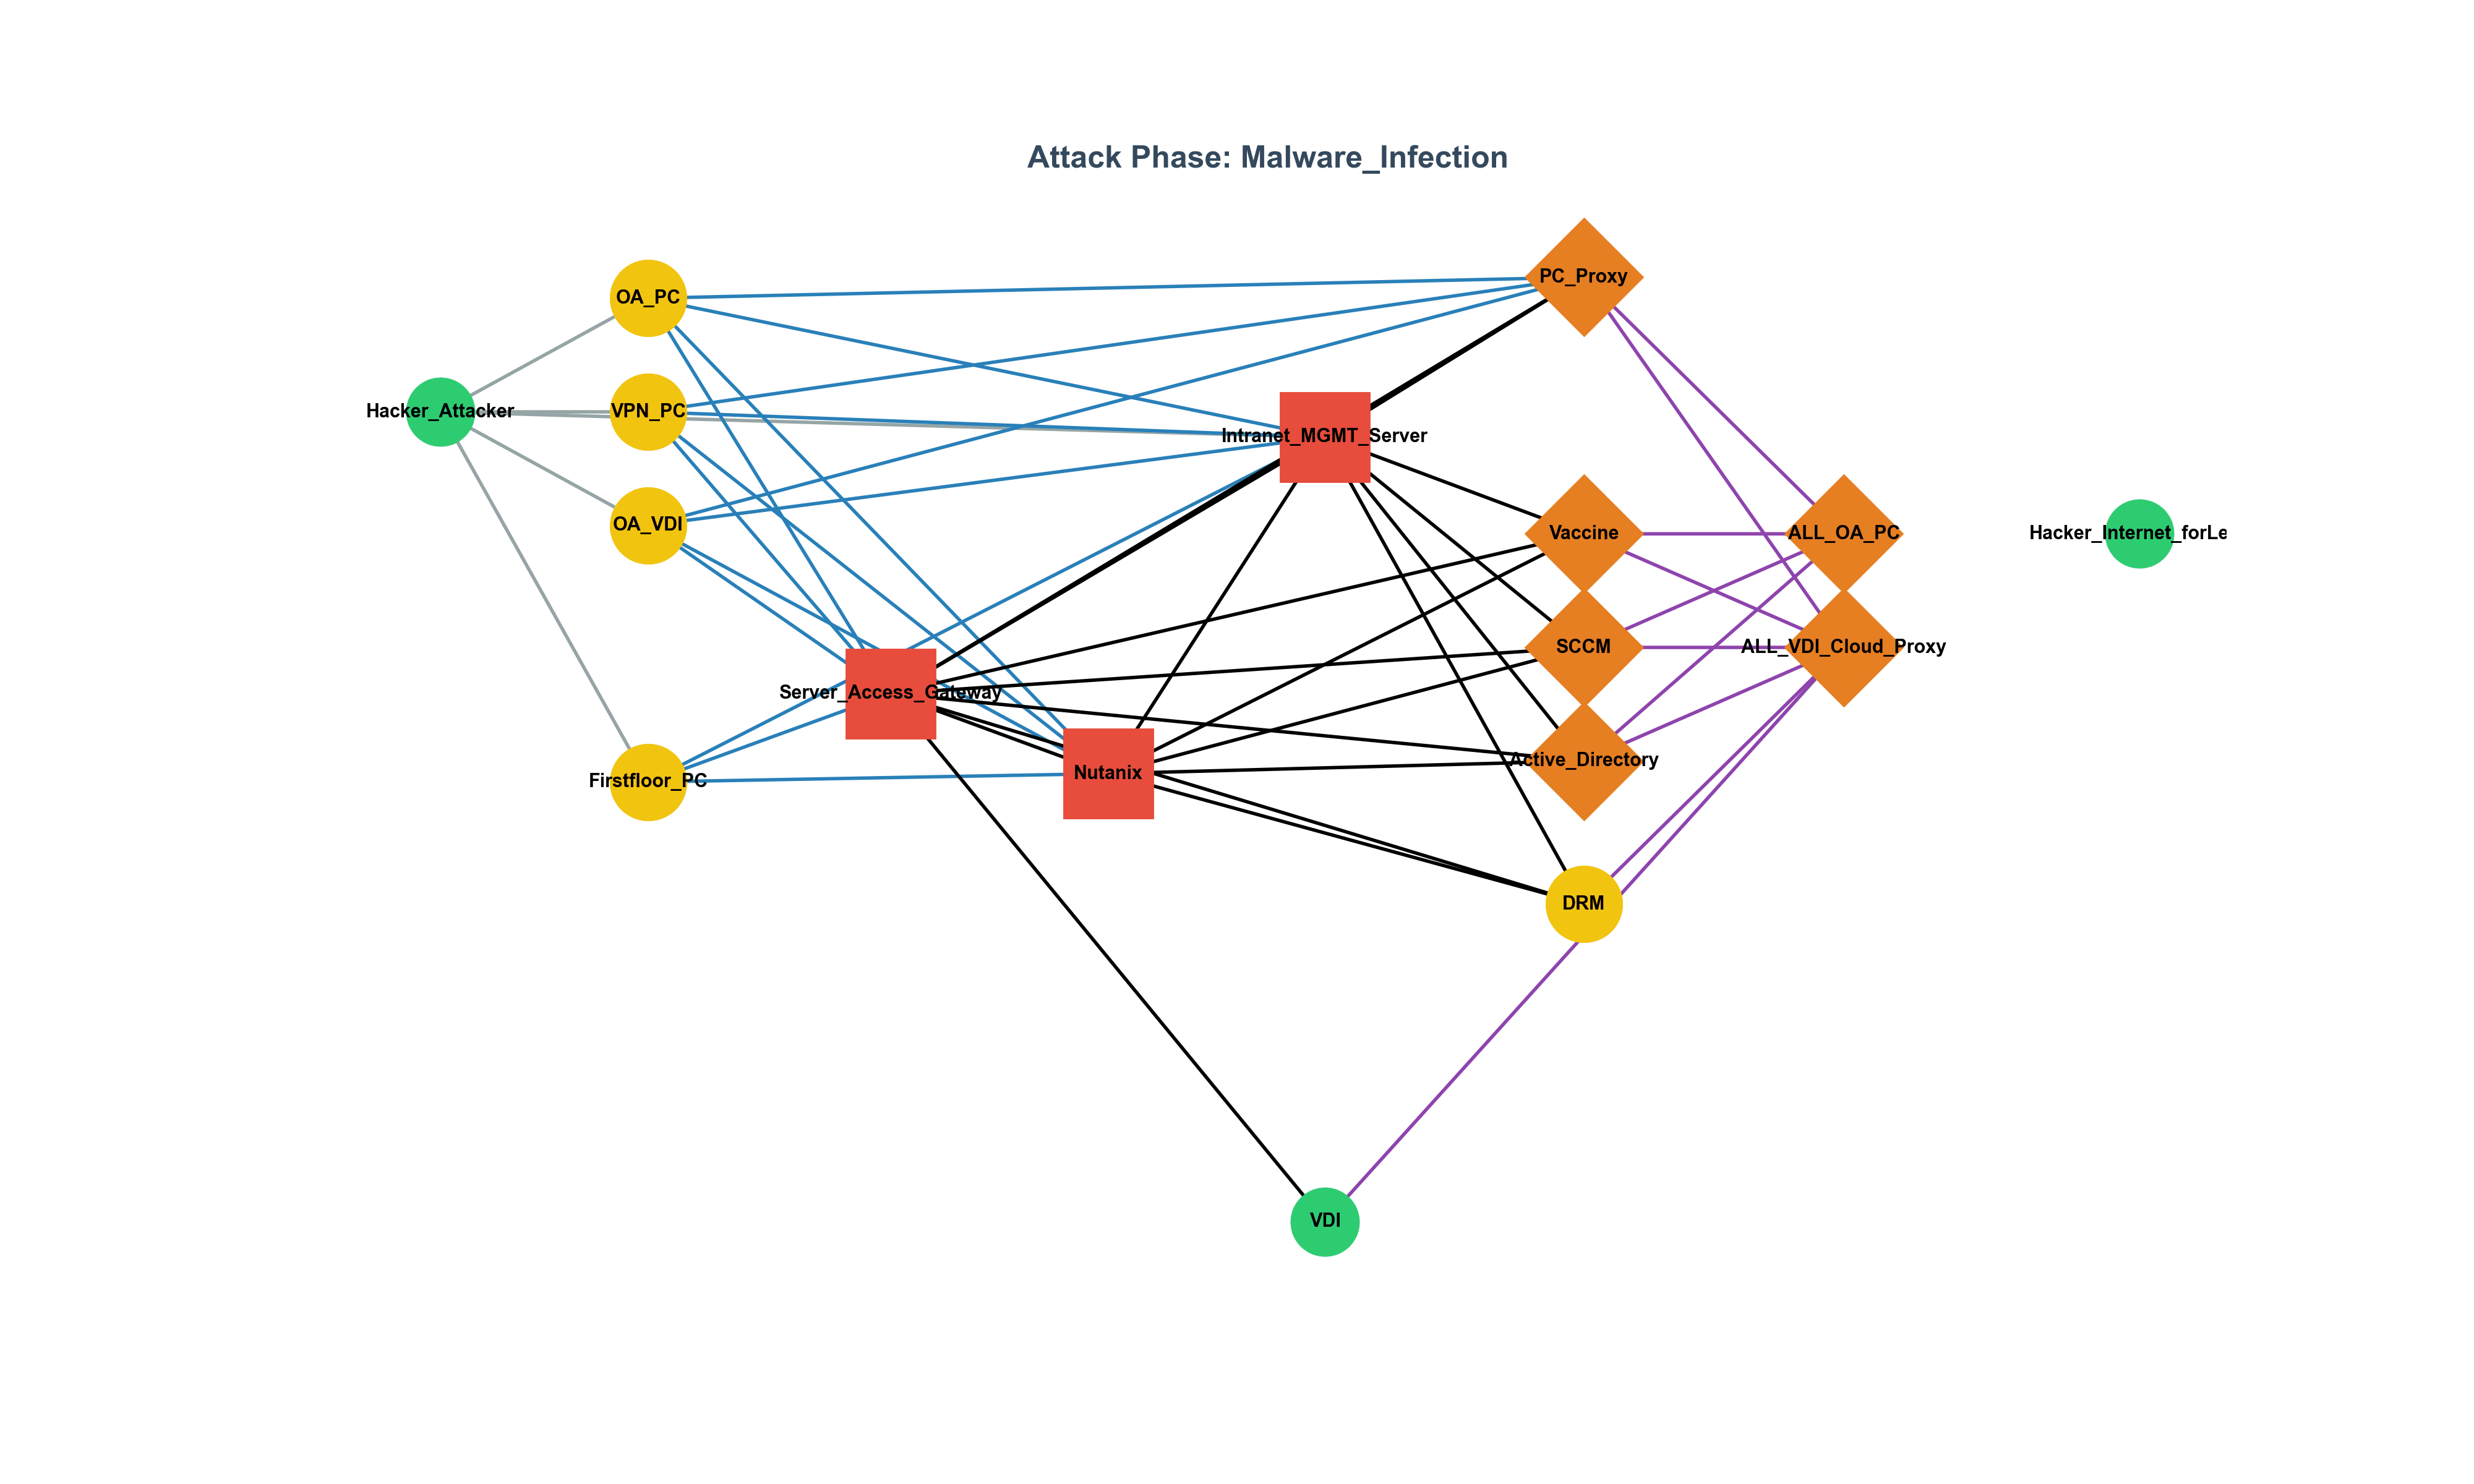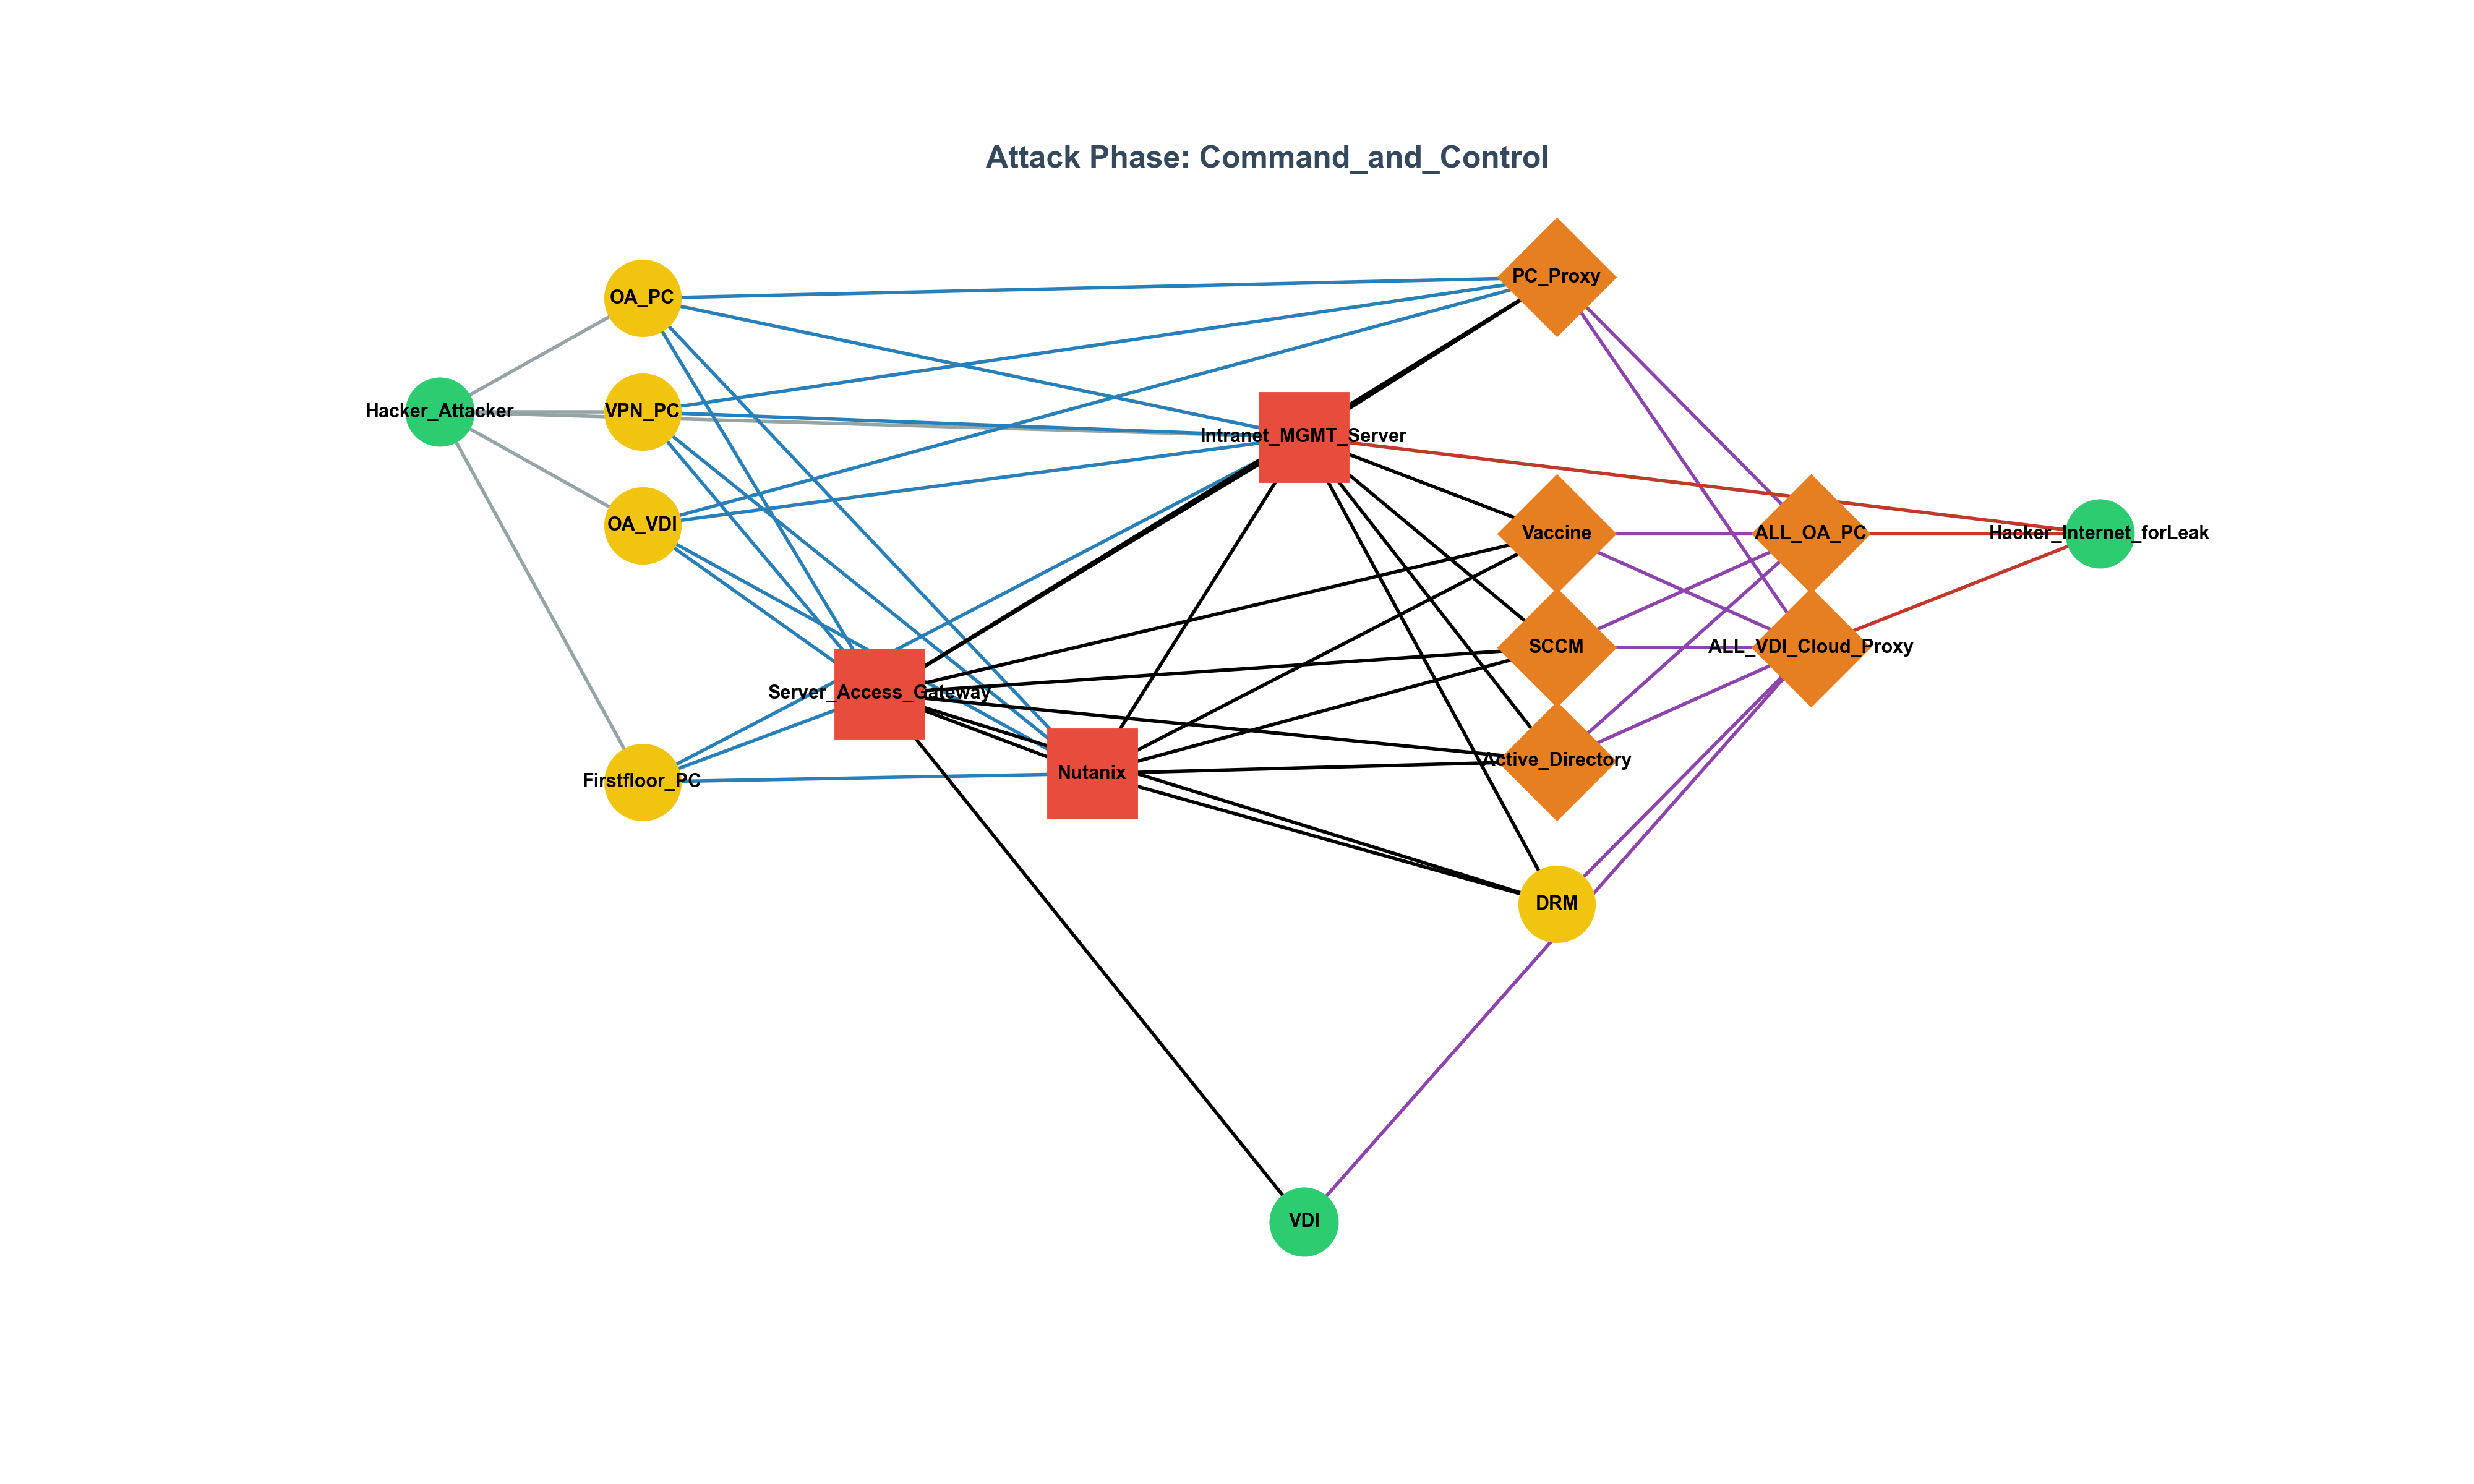
Finding Vulnerabilities Is Not the Same as Building Attack Scenarios

A practical method for modeling vulnerabilities as attacker-relevant security state transitions and combining human intuition with bounded AI search

August 3, 2026 · 24 min · 4951 words

Structure Builders Will Outlast Vulnerability Finders

18 years of vulnerability hunting distilled into one insight: the shift from individual instinct to scalable structure — and what AI means for those left standing.

April 2, 2026 · 8 min · 1641 words