The Visibility Principle: How Internal Vulnerability Visibility Shapes Remediation Behavior
How transparent internal vulnerability visibility drives remediation through accountability and deterrence without formal punishment.
Representative Foreword
The representative foreword of this blog: security now fails less at finding issues than at absorbing, sustaining, and acting on what has already been found.
This essay frames the entire site first. The posts on technical analysis, method, and governance all start from this same problem statement.
Detection, Method, Governance
How transparent internal vulnerability visibility drives remediation through accountability and deterrence without formal punishment.
Why continuous attack surface management is critical in 2025, covering AI-driven discovery, shadow IT, and zero trust integration.
Analysis of the 2025 KakaoPay breach exposing 40M users’ data, and why formal consent fails without AI-based DPIA and civic oversight.
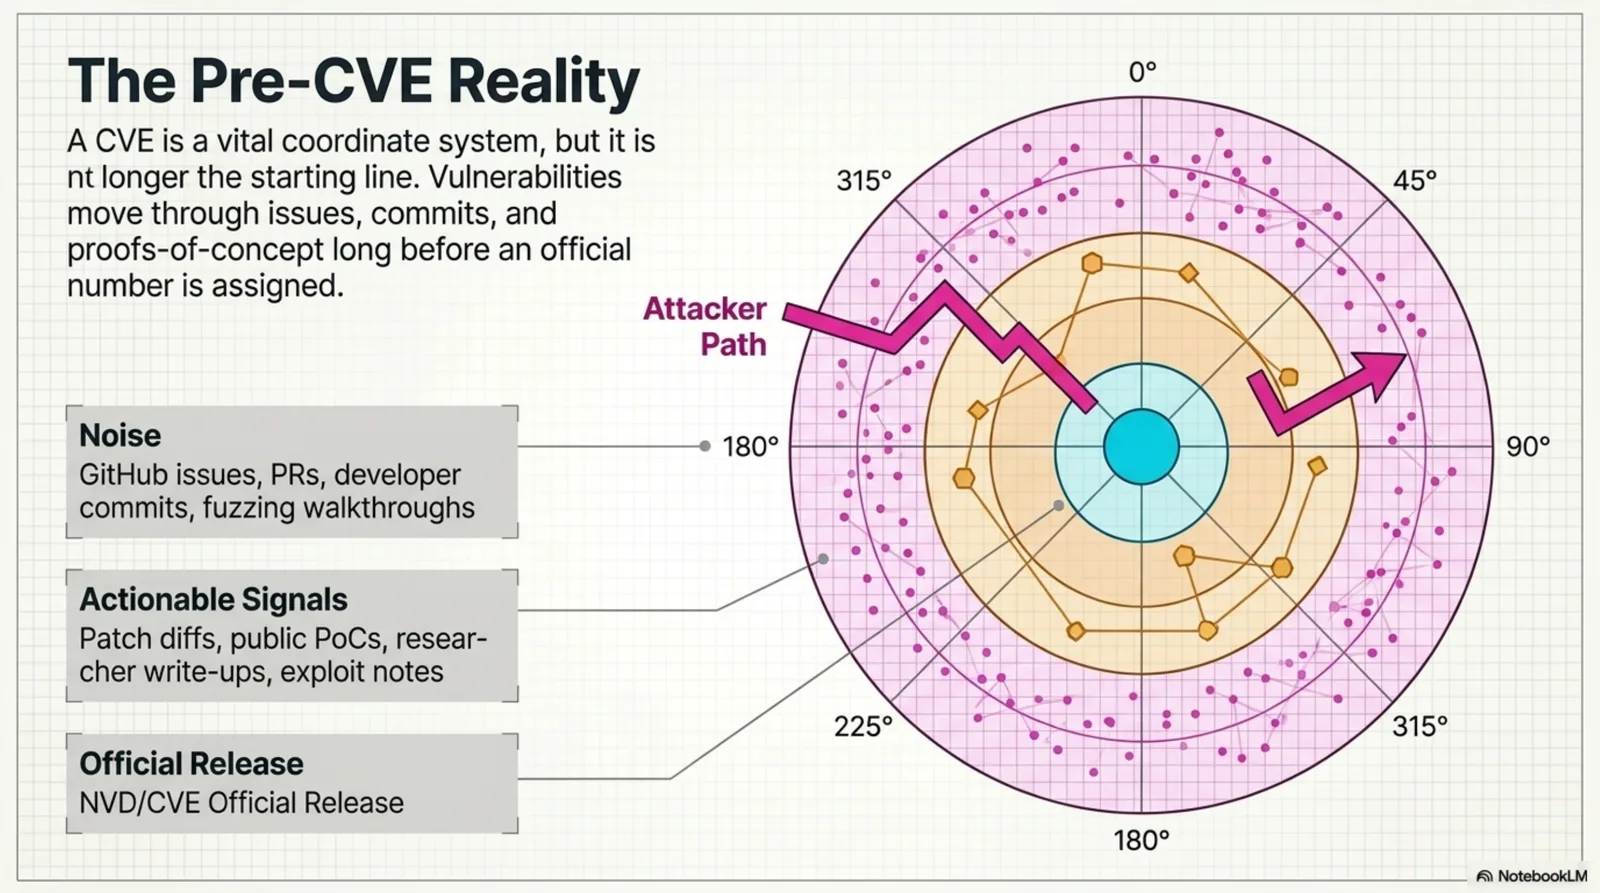
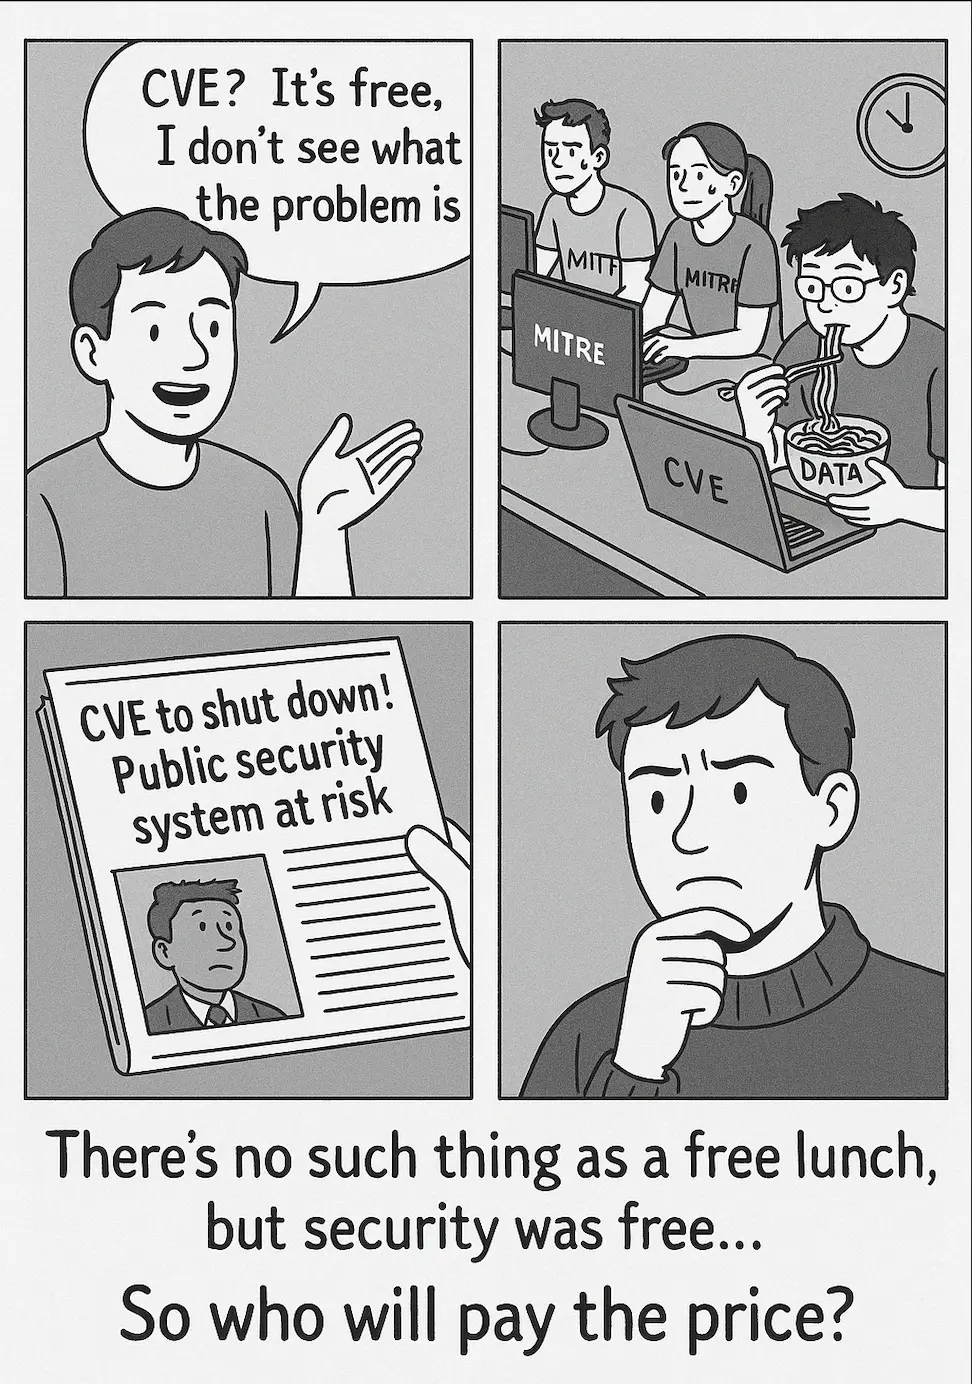
The CVE system nearly collapsed in 2025. Who should fund public cybersecurity infrastructure when free-riding is no longer sustainable?
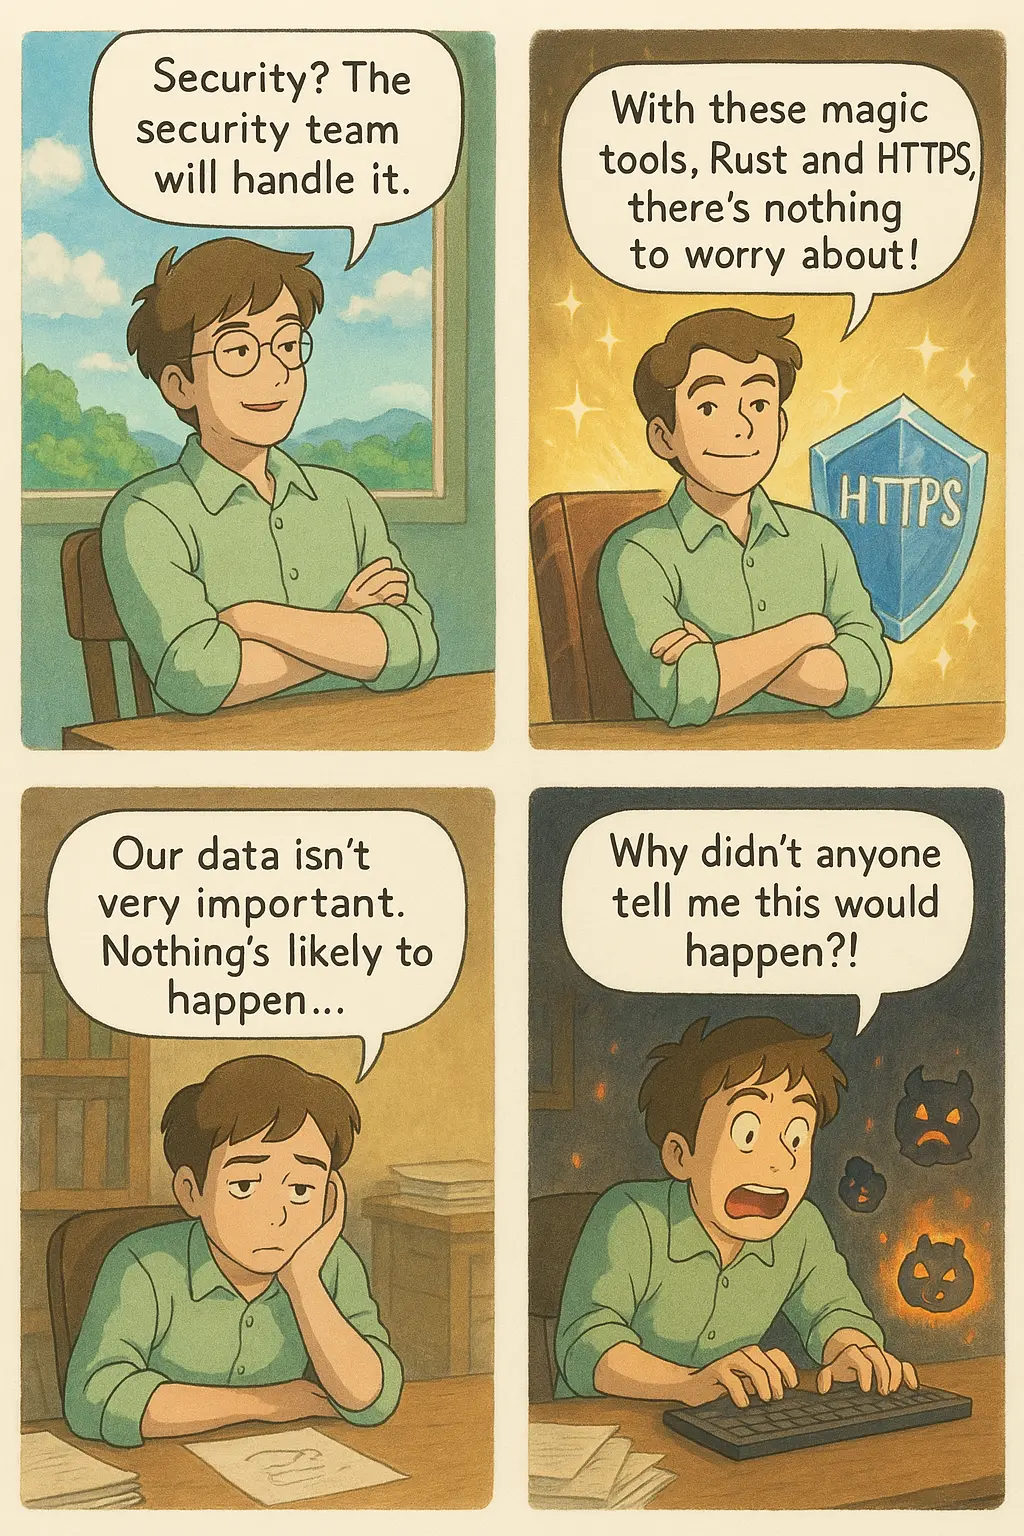
Debunking developer security myths around responsibility deflection, tech overconfidence, and risk underestimation with real-world examples.
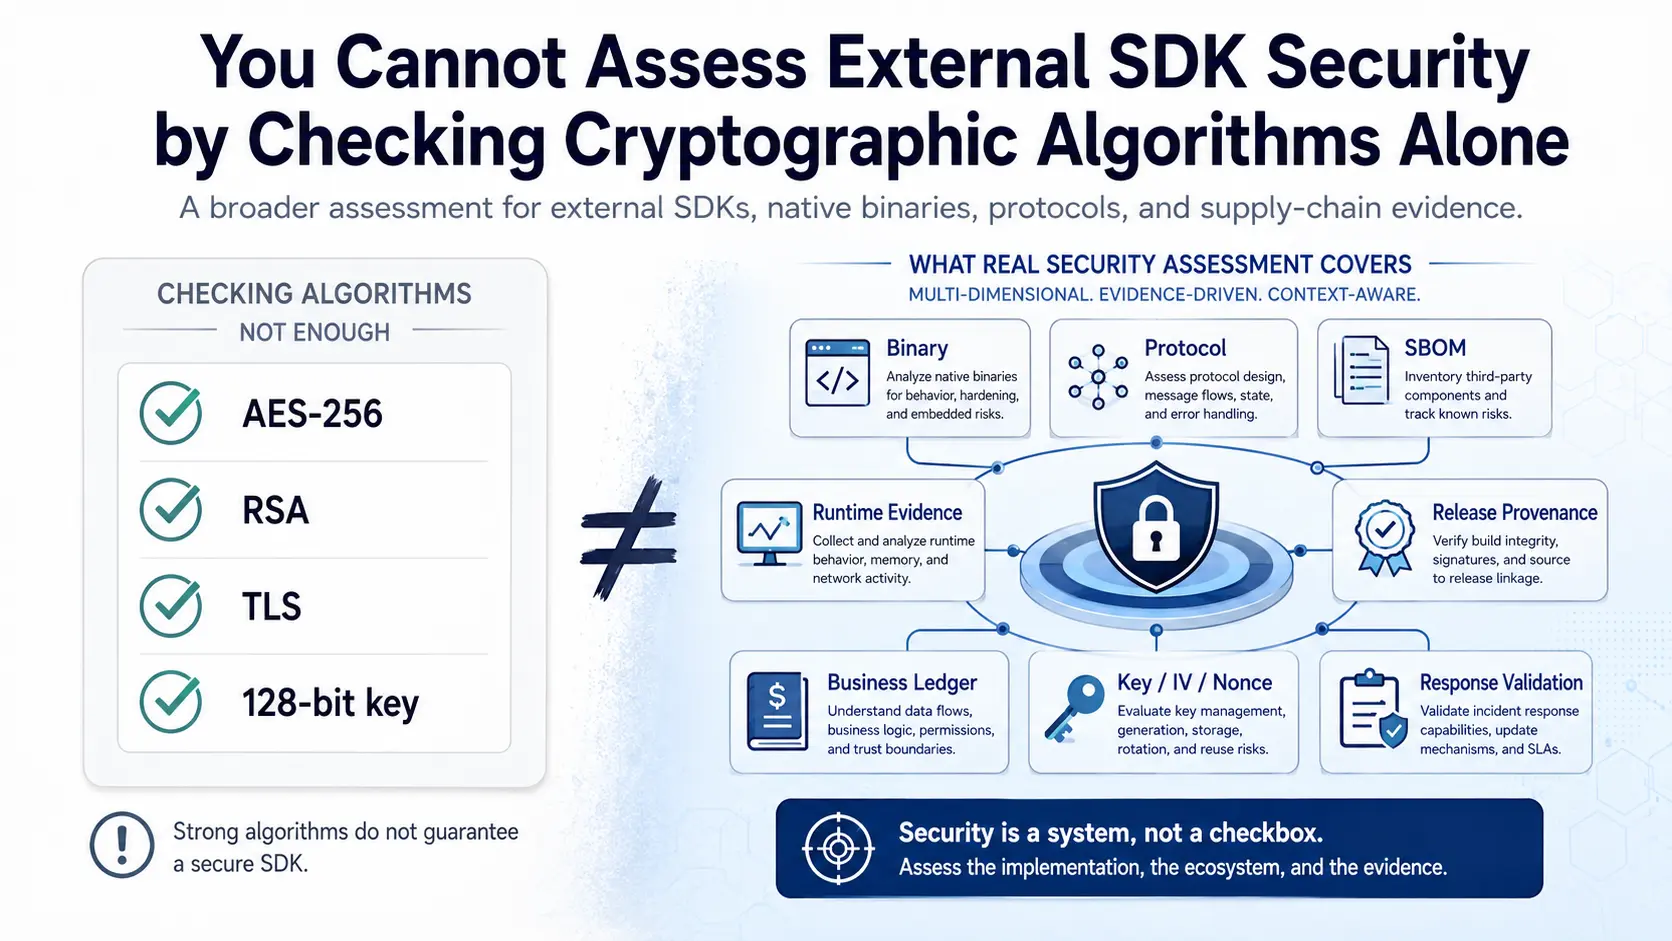
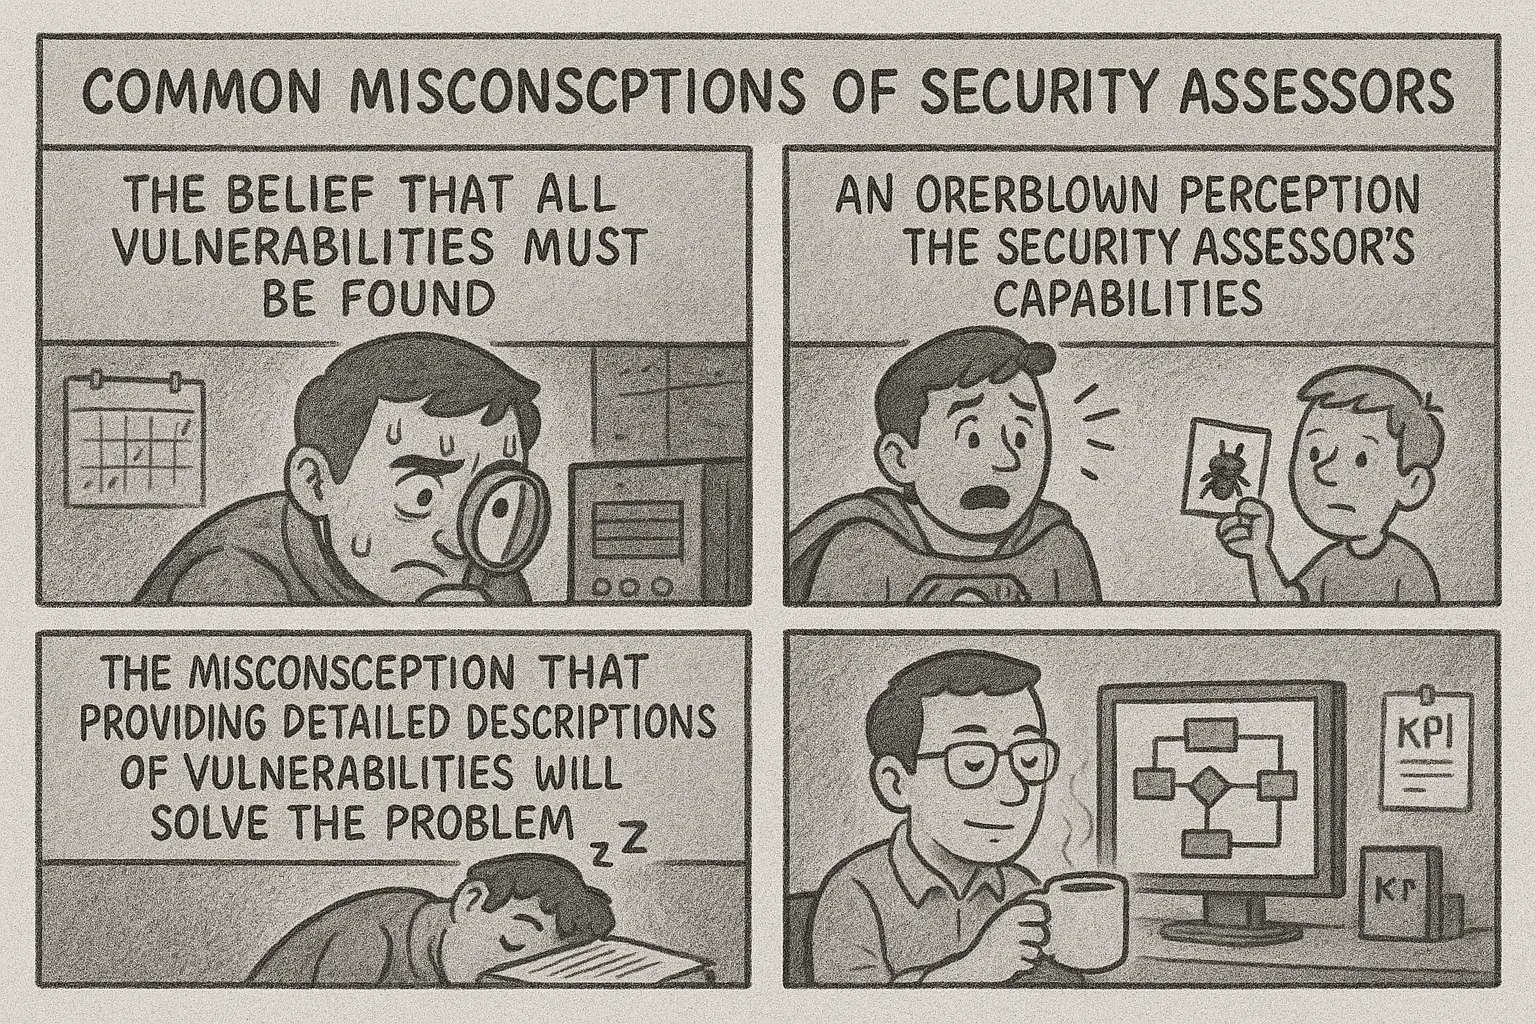
Three common misconceptions that weaken security assessments and strategies to build repeatable, effective vulnerability evaluation.