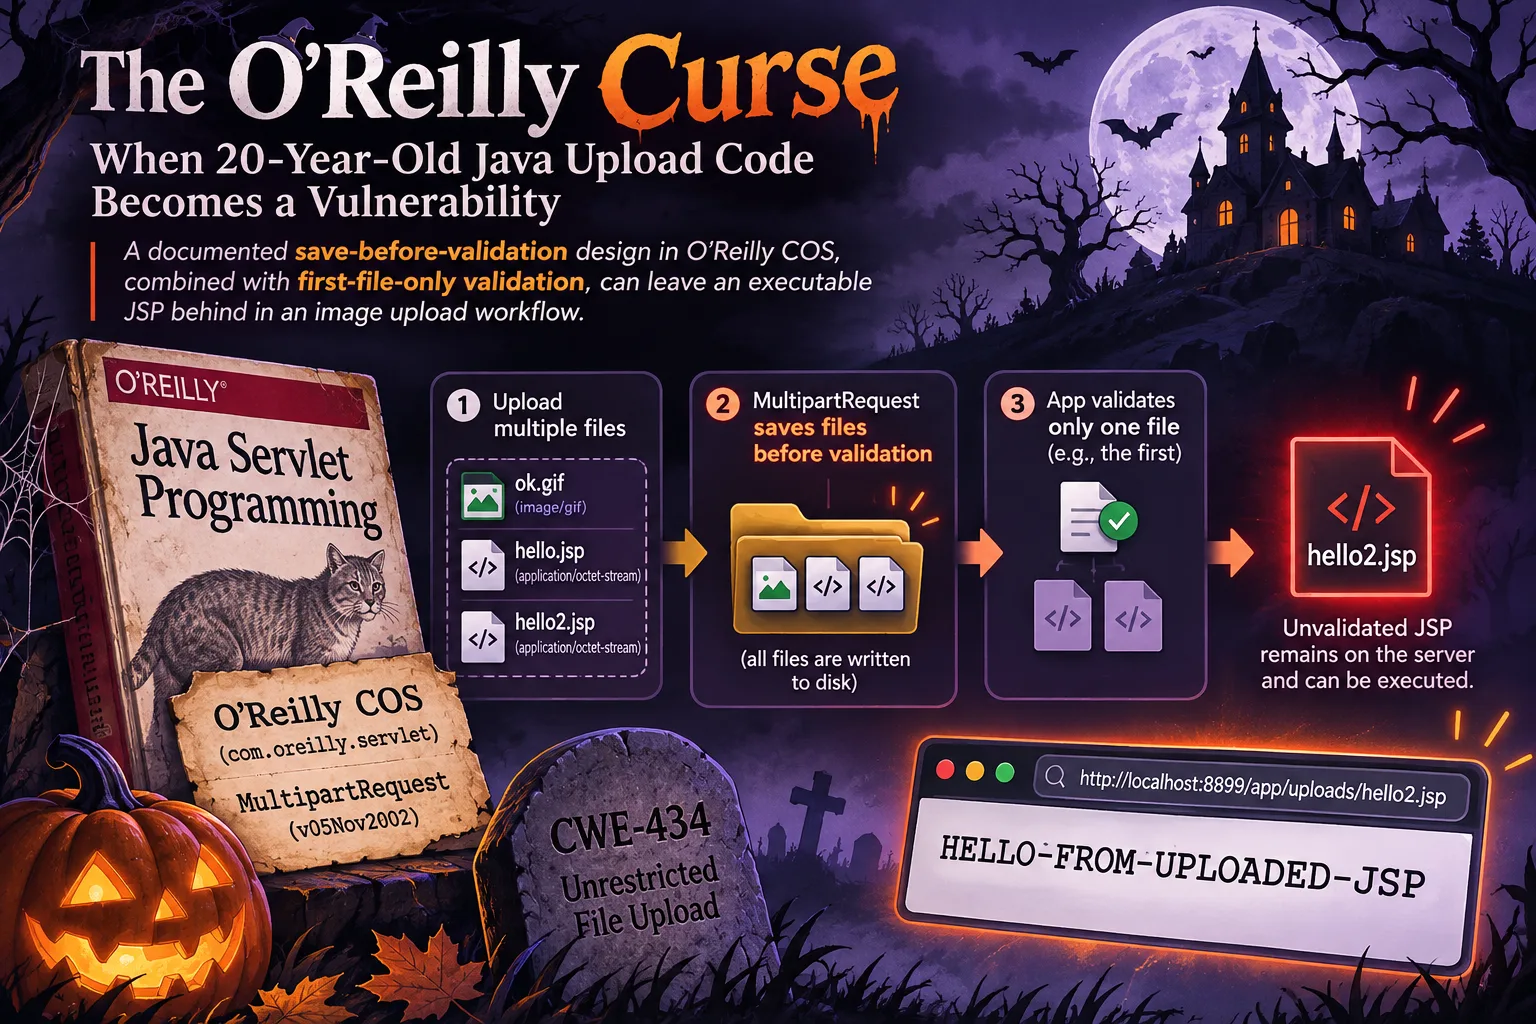


The O’Reilly Curse: When 20-Year-Old Java Upload Code Becomes a Vulnerability
A documented save-before-validation design in O’Reilly COS MultipartRequest, combined with first-file-only application validation, can leave an executable JSP behind in an image-upload flow. A CWE-434 case study through code, a reproduction walkthrough, and the proper fix.