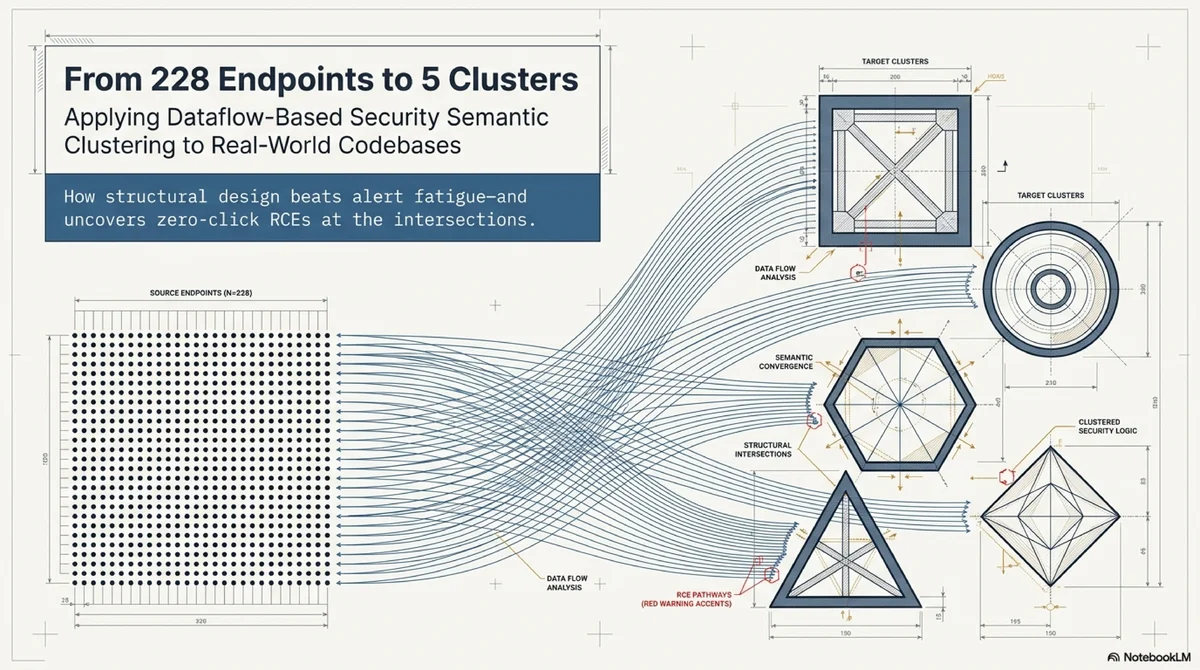
How I Turned 228 Endpoints into 5 Clusters
A practical account of applying dataflow-based clustering to a real codebase — reducing 228 endpoints to 5 reviewable clusters, and finding an RCE chain in the cross-section.
Representative Foreword
The representative foreword of this blog: security now fails less at finding issues than at absorbing, sustaining, and acting on what has already been found.
This essay frames the entire site first. The posts on technical analysis, method, and governance all start from this same problem statement.
Detection, Method, Governance
A practical account of applying dataflow-based clustering to a real codebase — reducing 228 endpoints to 5 reviewable clusters, and finding an RCE chain in the cross-section.
How Korea’s CaaS supply chain reproduces itself through the recycling loop of points, gift cards, and crypto — and why defending against it requires reading the entire behavioral network, not just the login page.
18 years of vulnerability hunting distilled into one insight: the shift from individual instinct to scalable structure — and what AI means for those left standing.
A practical look at an audio CAPTCHA bypass PoC built with Playwright, Whisper, and Page-Agent, plus the login defenses that still matter after CAPTCHA falls.
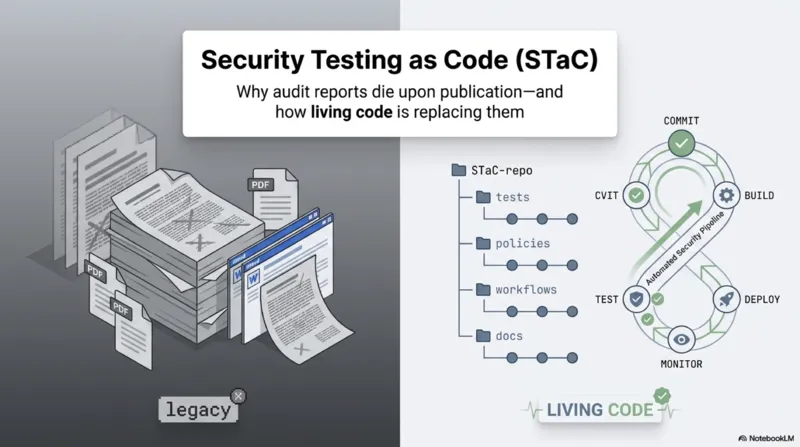
We point out the limitations of traditional security diagnostic reports and share the necessity and practical application cases of ‘Security Testing as Code’, managing diagnostic results not as ‘documents’ but as ’executable code (PoC)’.
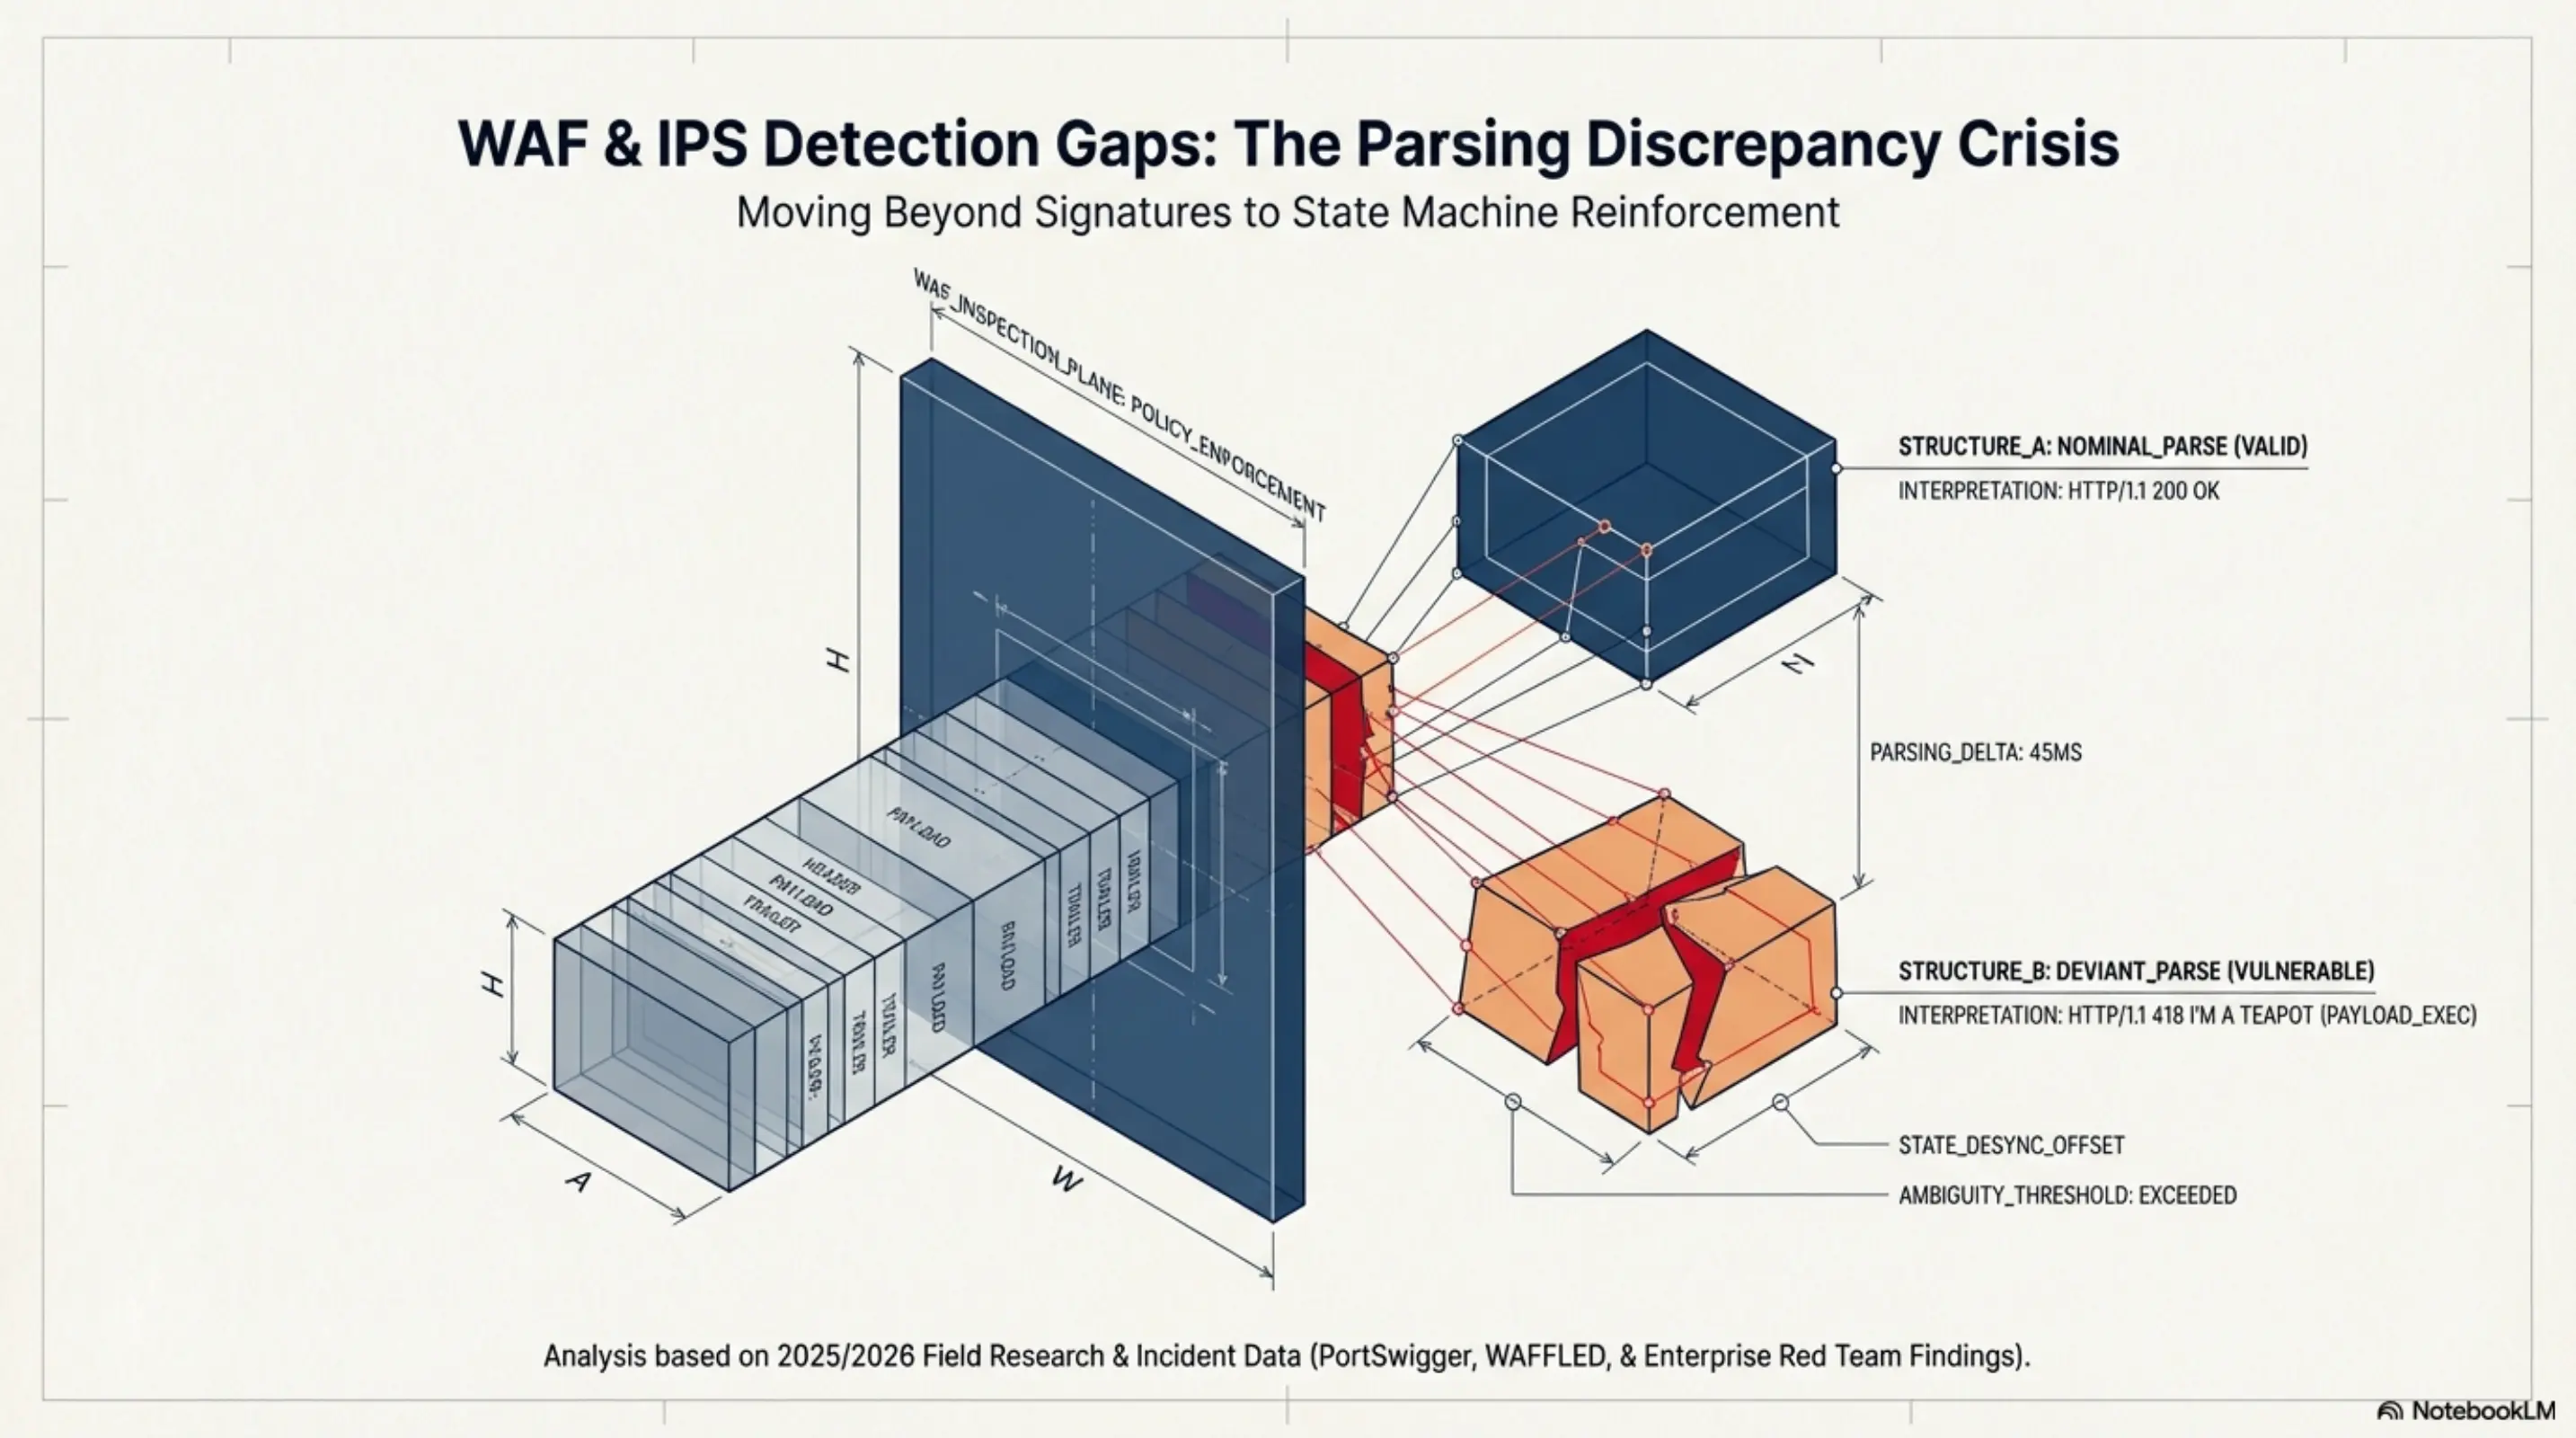
Structural analysis of WAF, IPS, and IDS detection gaps from parsing discrepancies, with a practical remediation taxonomy.
Why continuous attack surface management is critical in 2025, covering AI-driven discovery, shadow IT, and zero trust integration.
Theoretical RCE risks in OpenStack Nova’s exception serialization via oslo.messaging, with PoC scenarios and defense patterns.
In-depth analysis of the 2025 SKT breach, telecom authentication mechanisms, and 5G SA vs NSA security architecture differences.
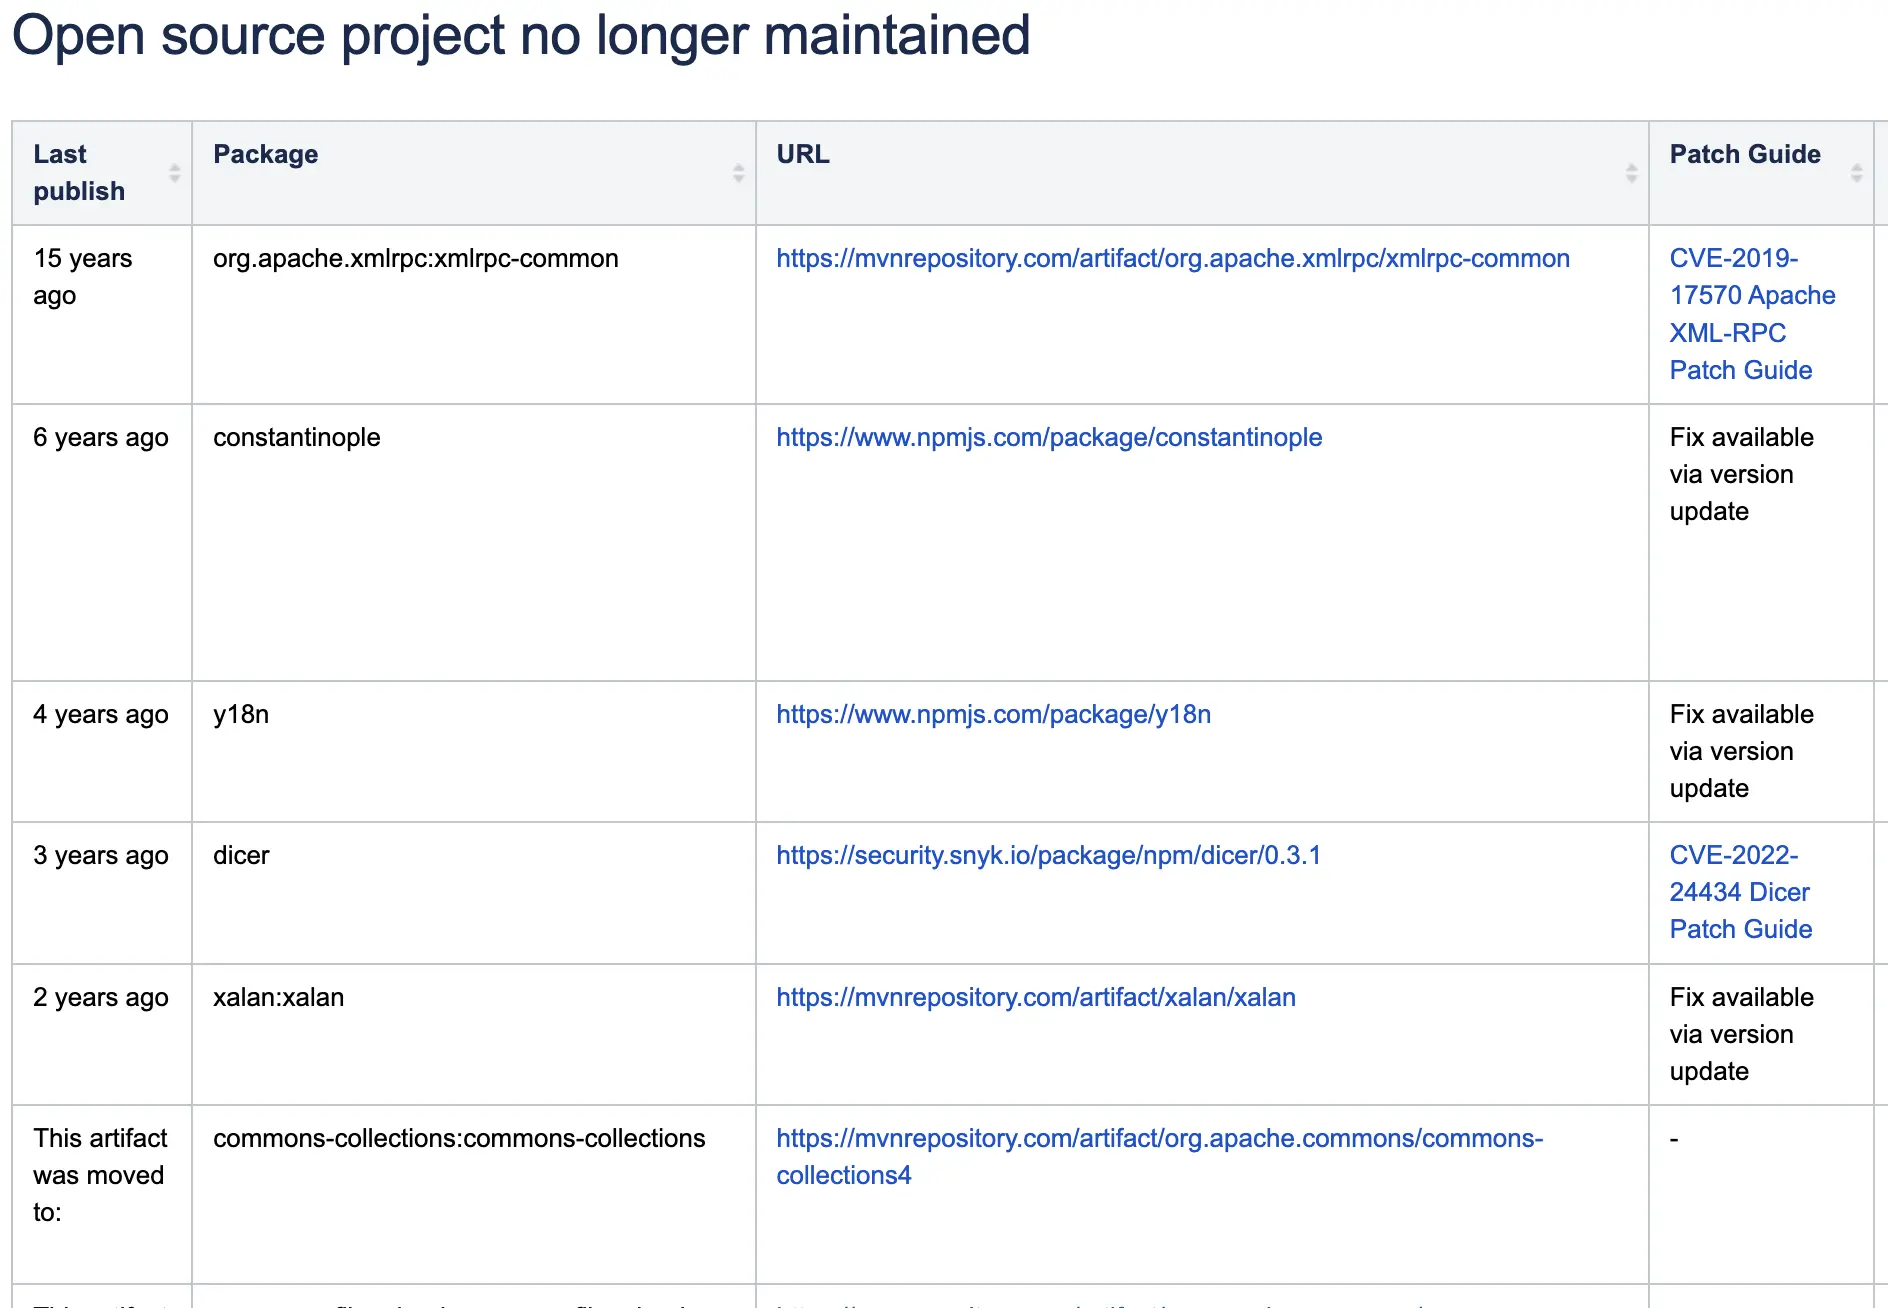
Technical analysis of CVE-2019-17570 deserialization RCE in Apache XML-RPC, with patch comparison and secure implementation guidance.