
Finding Vulnerabilities Is Not the Same as Building Attack Scenarios
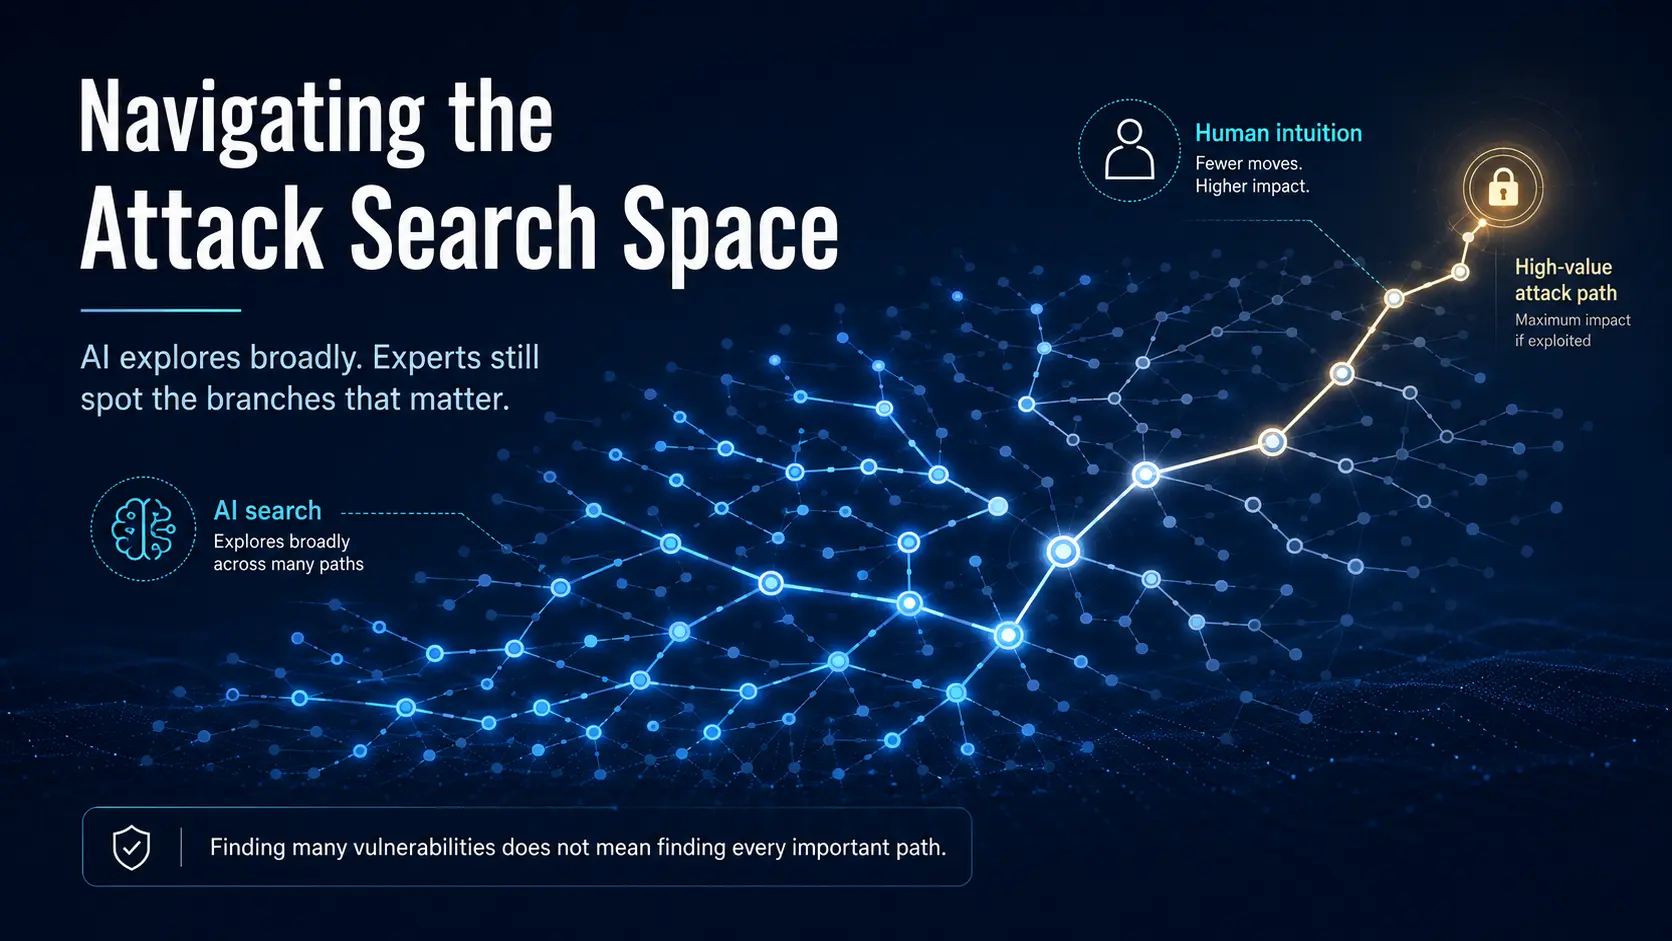
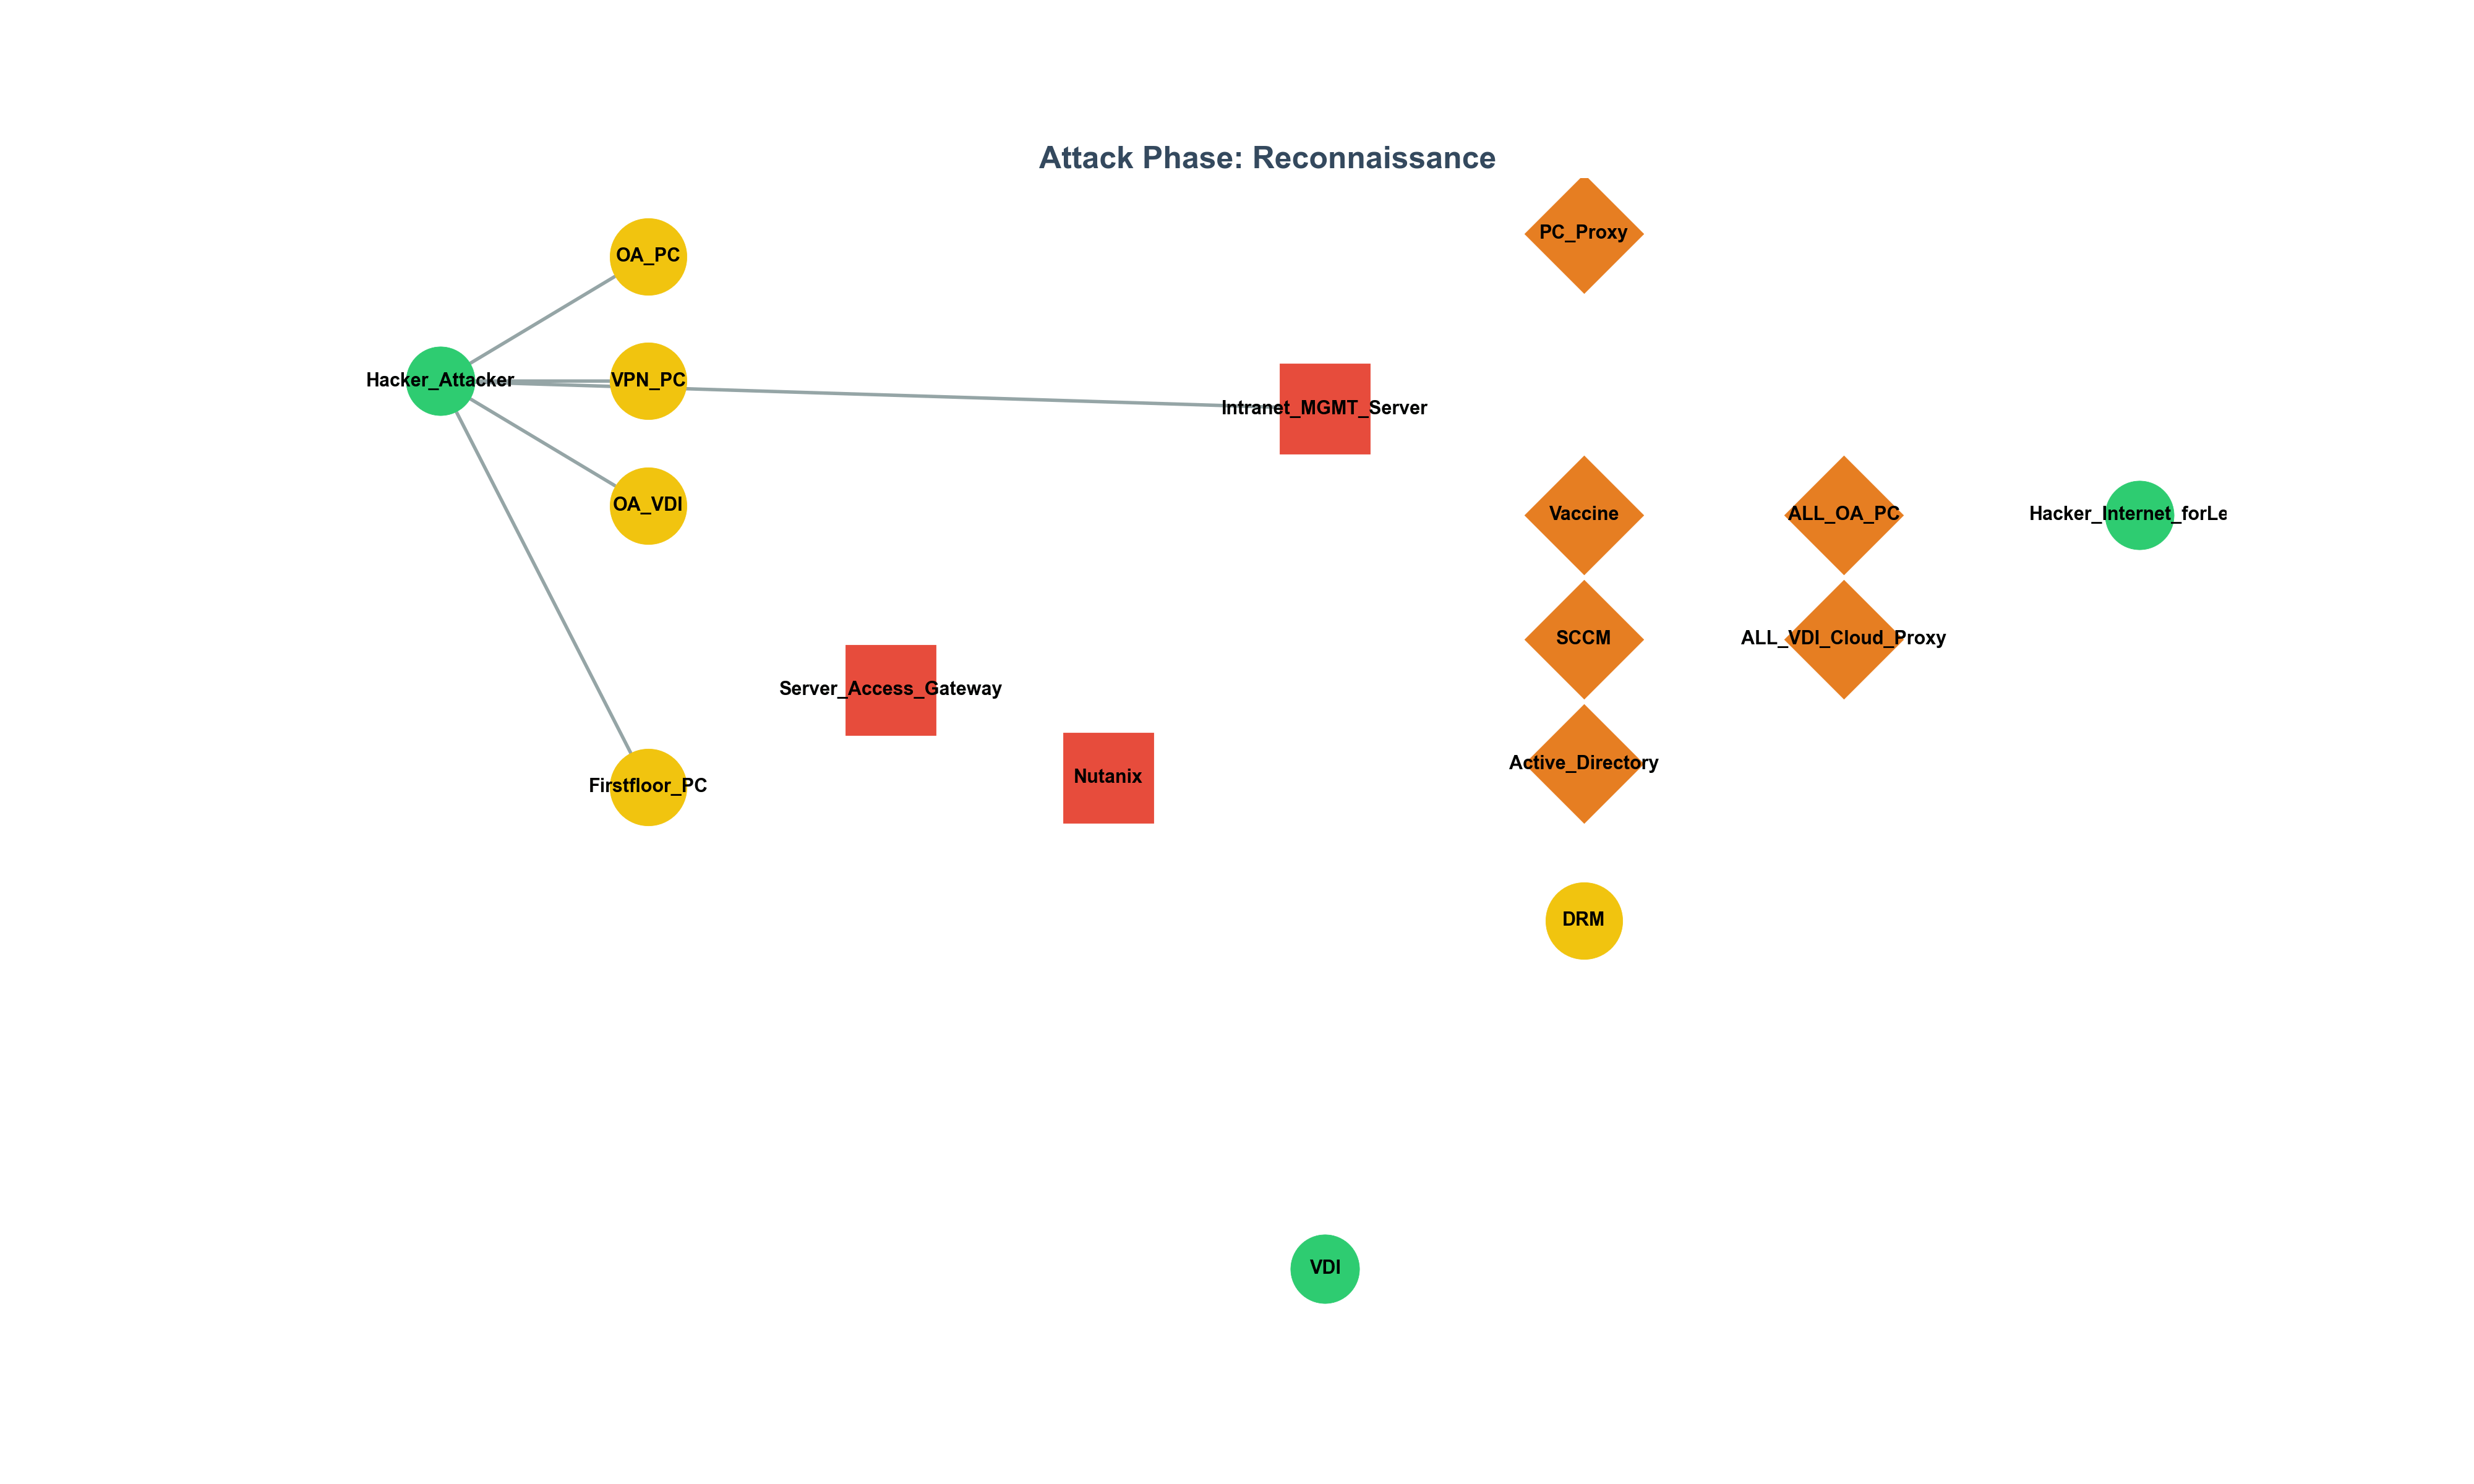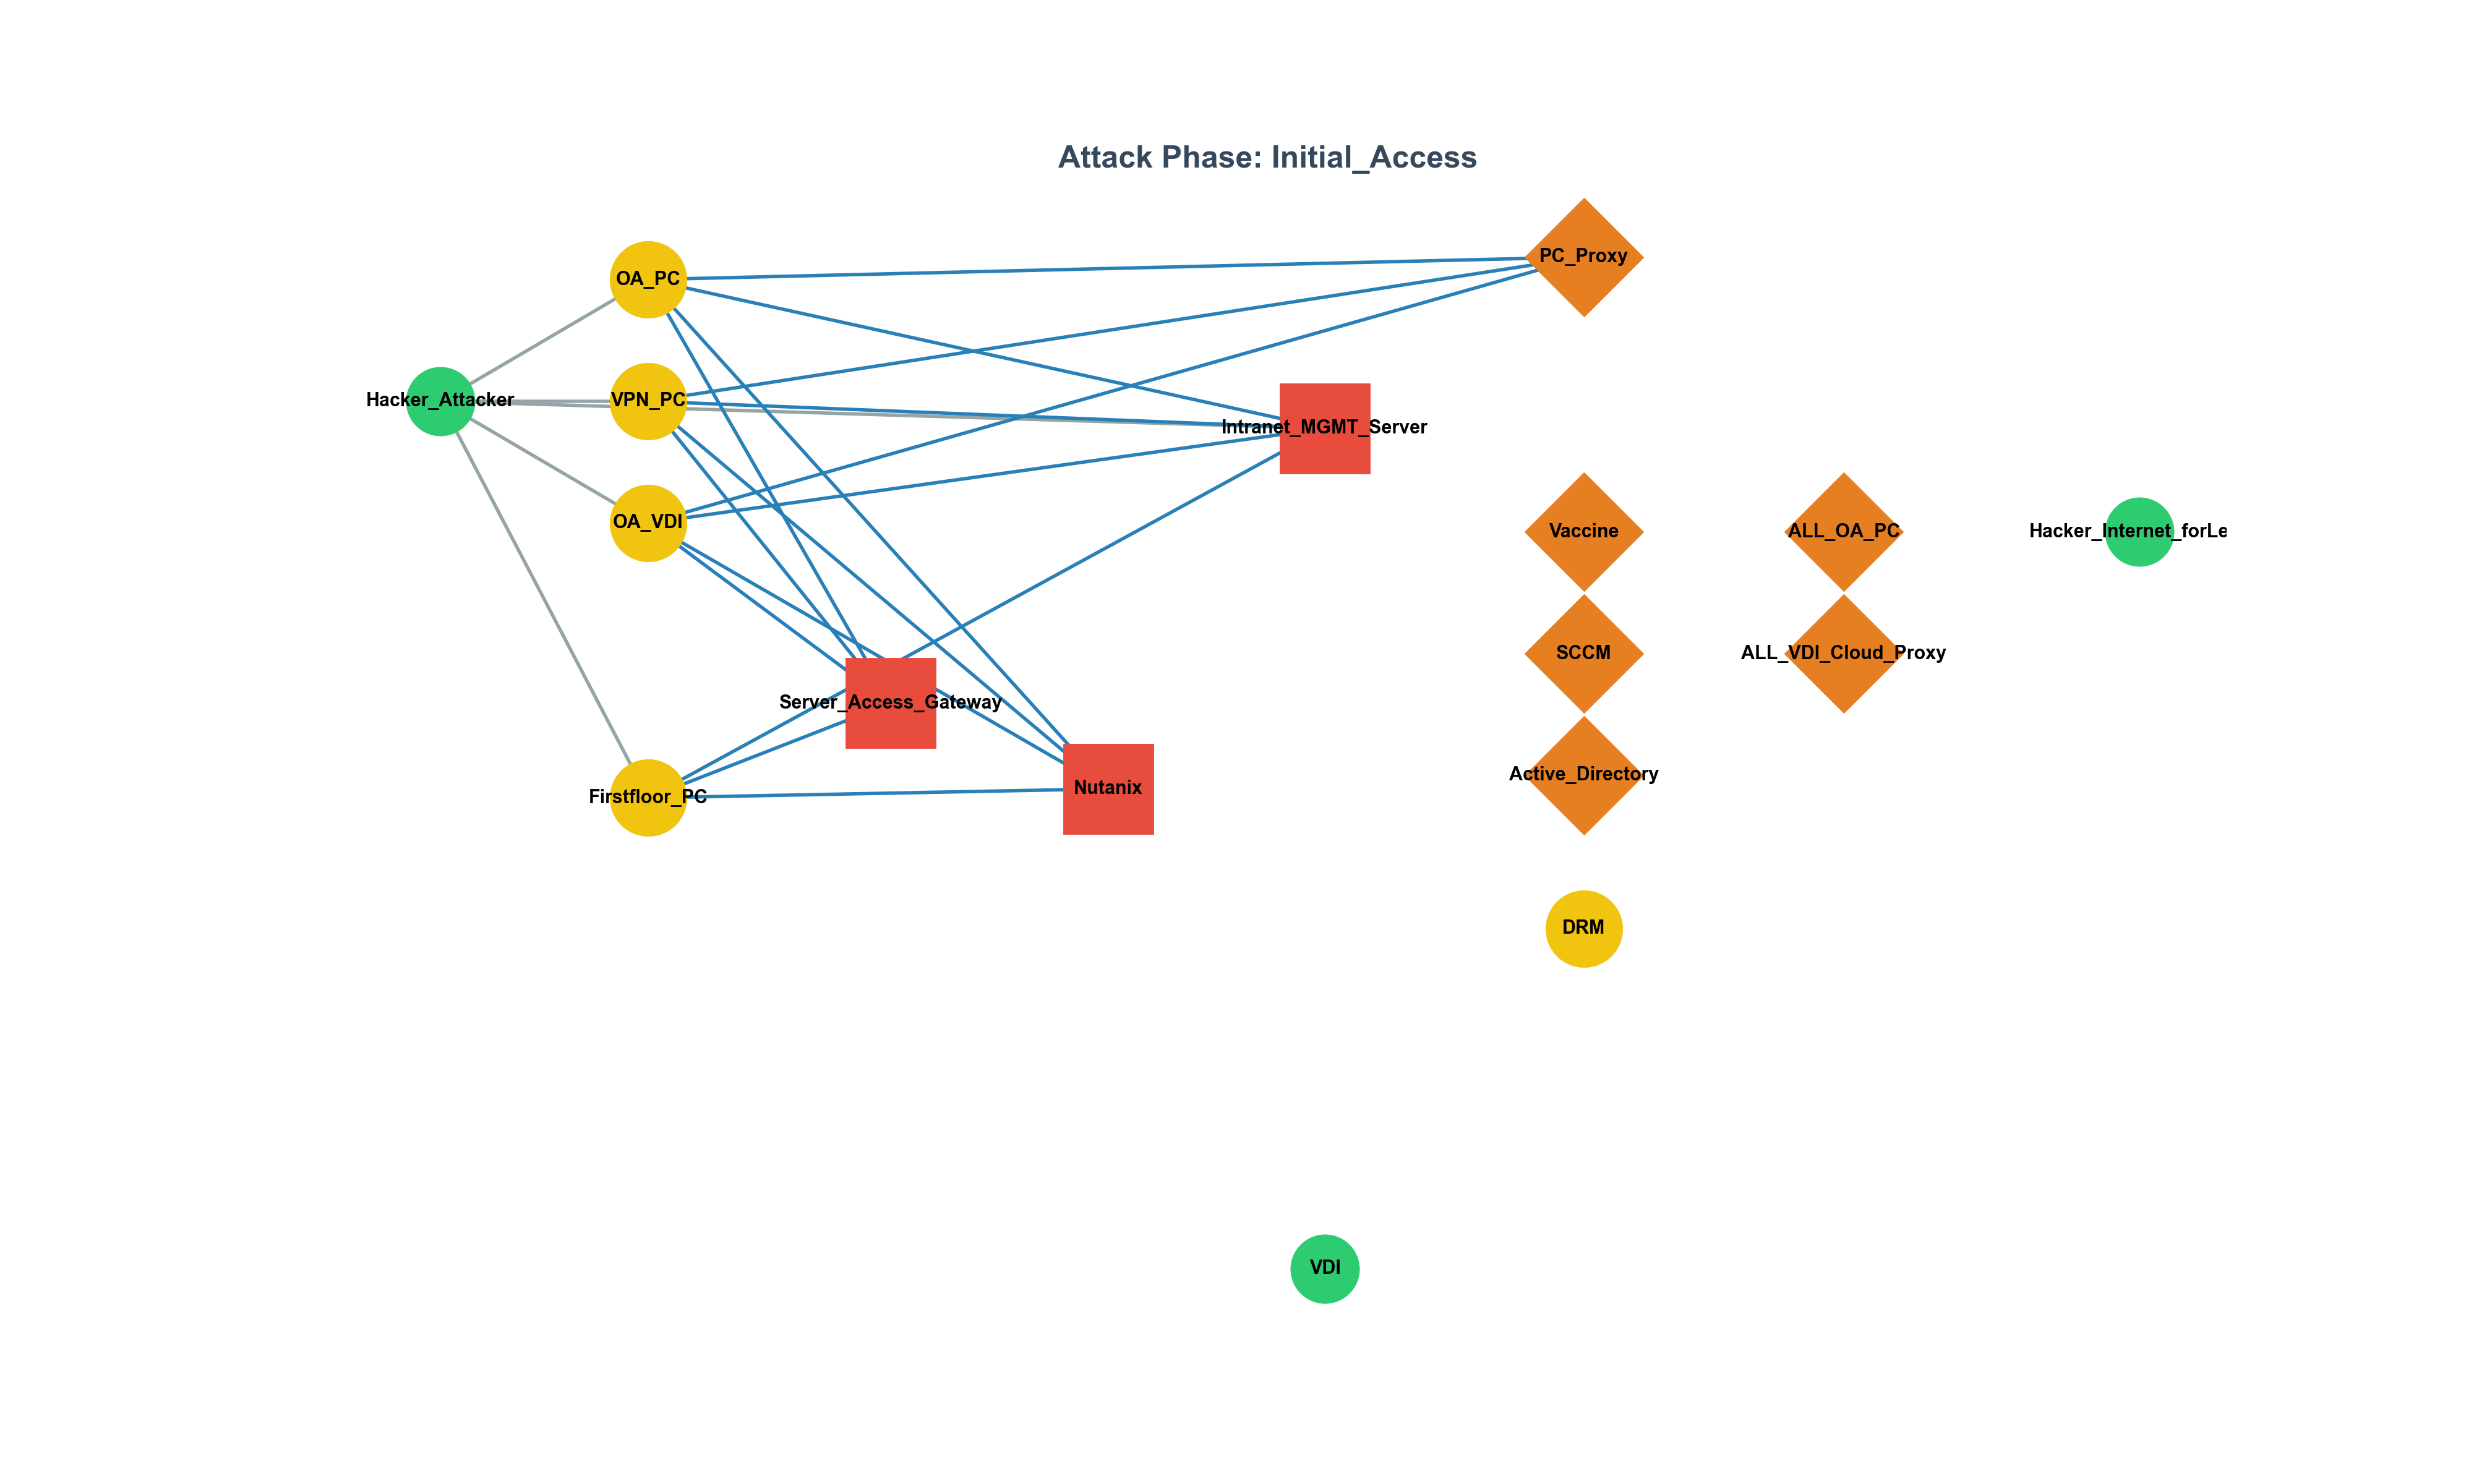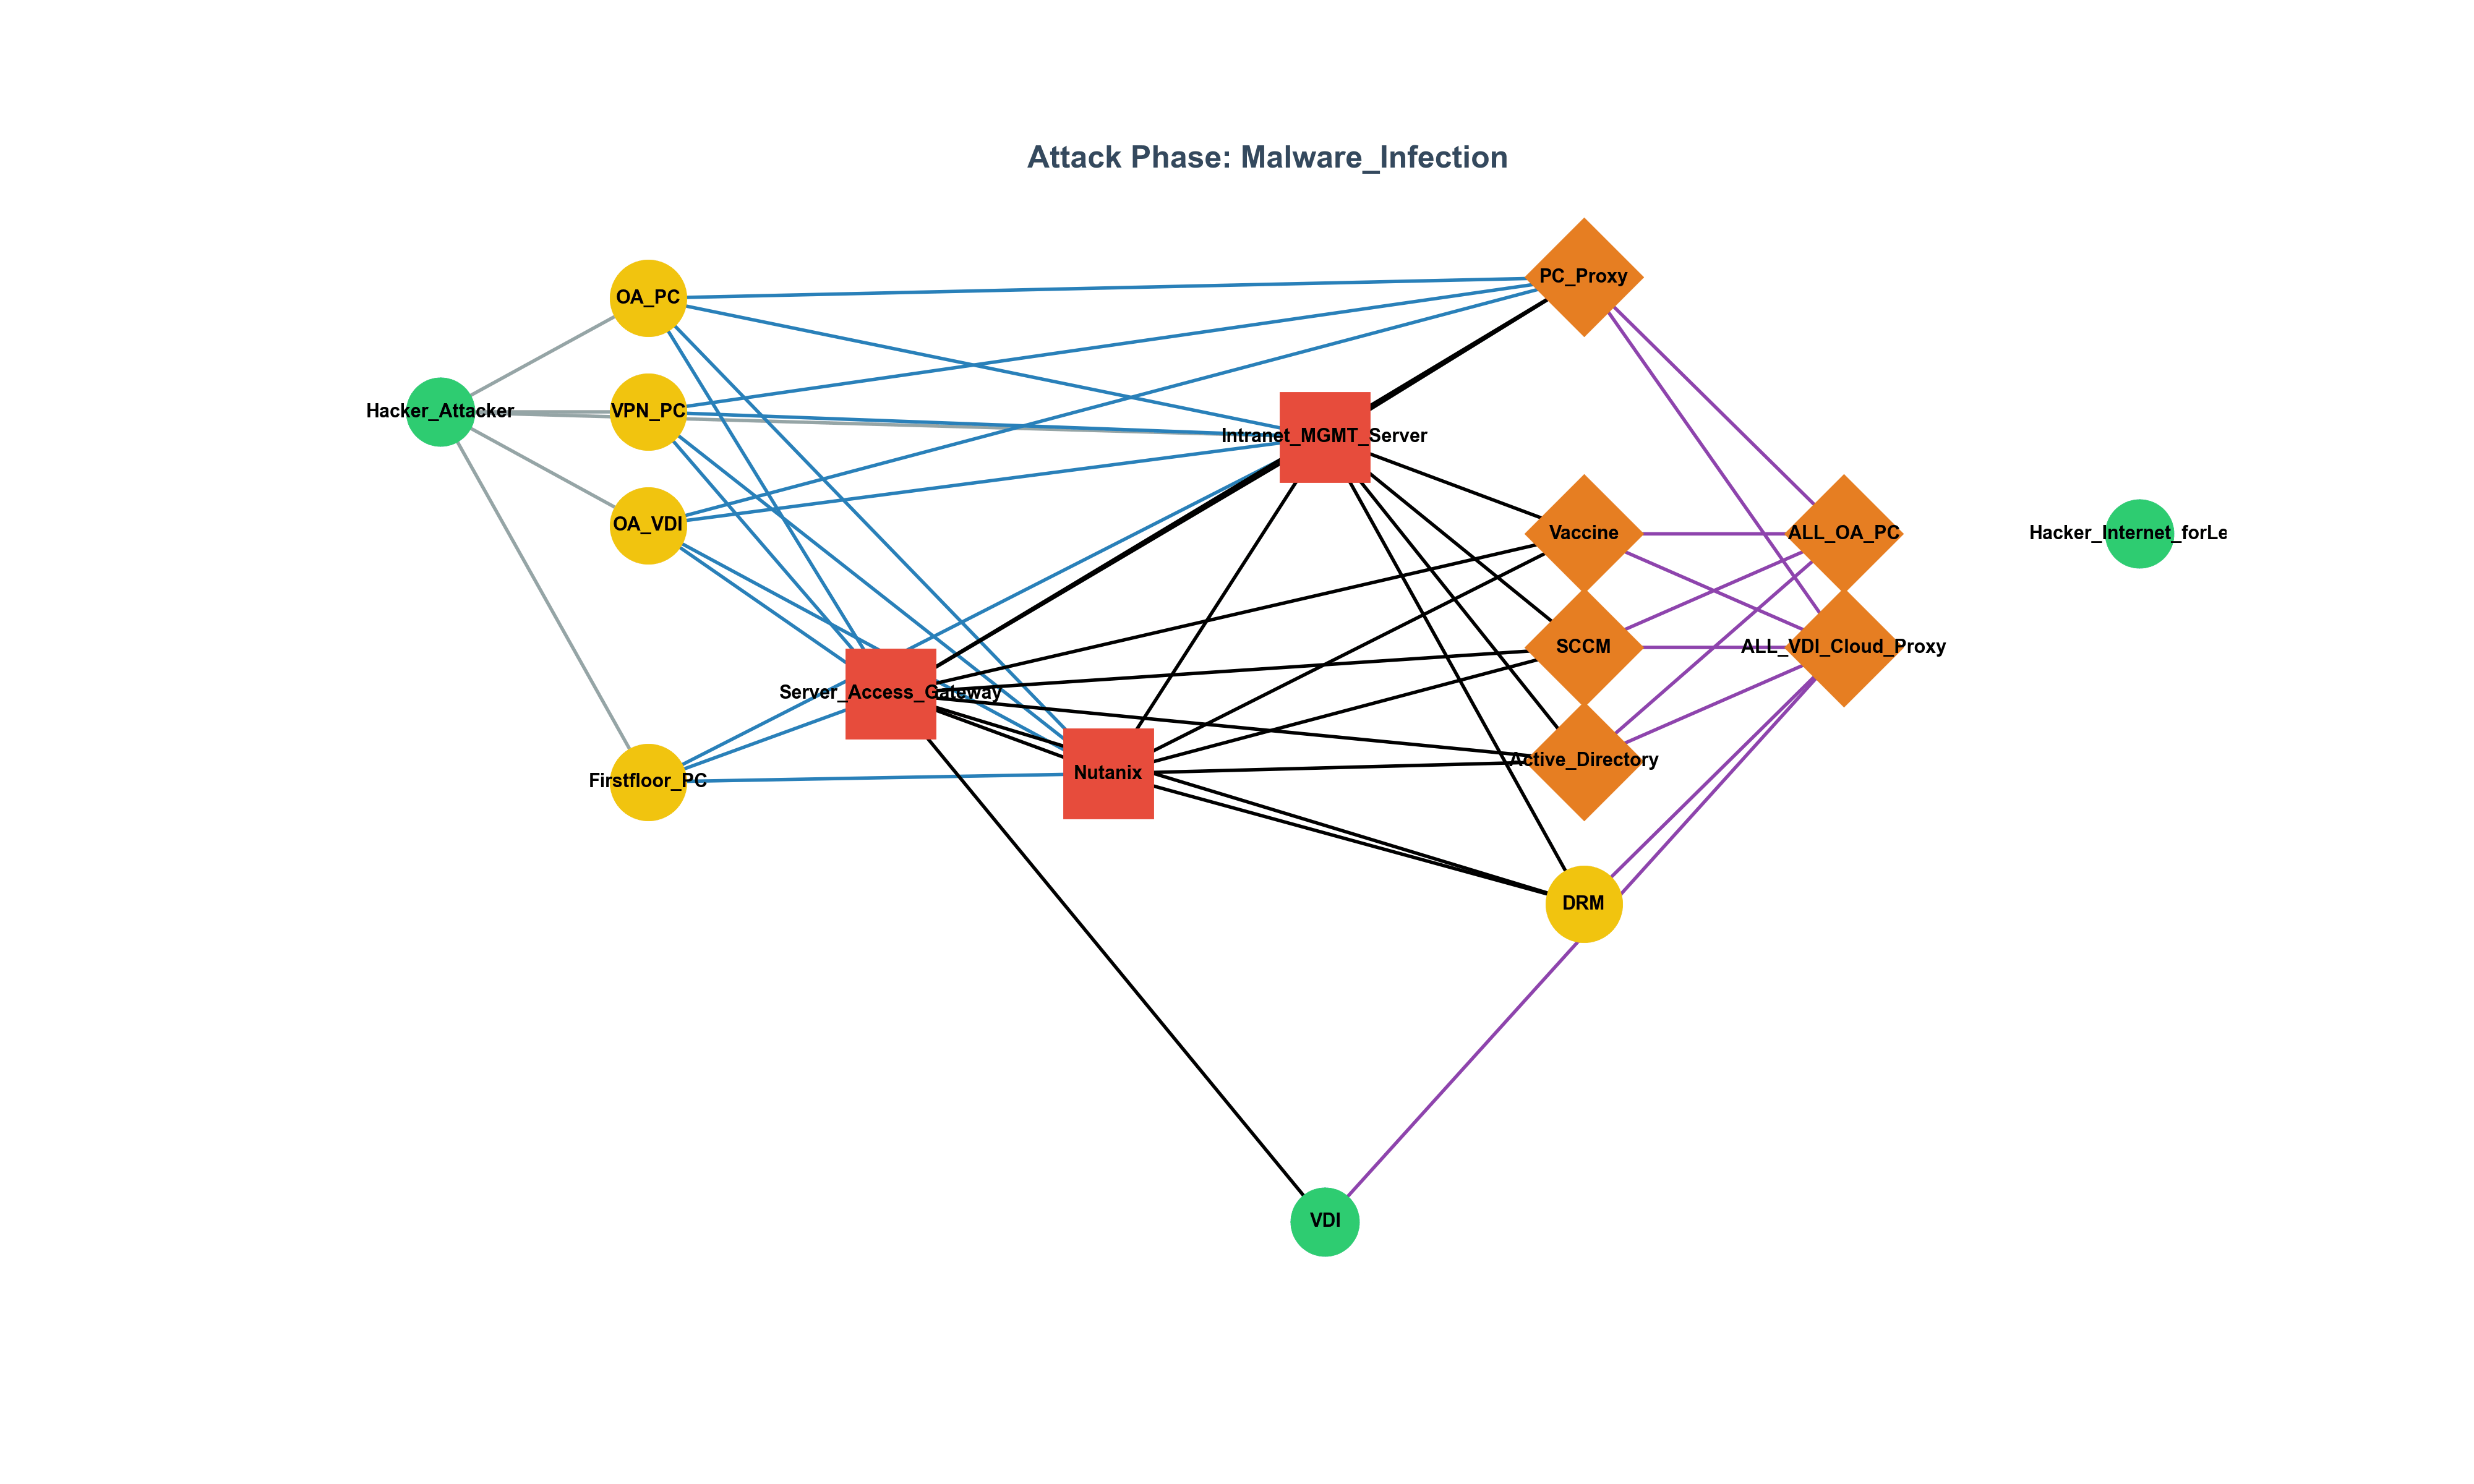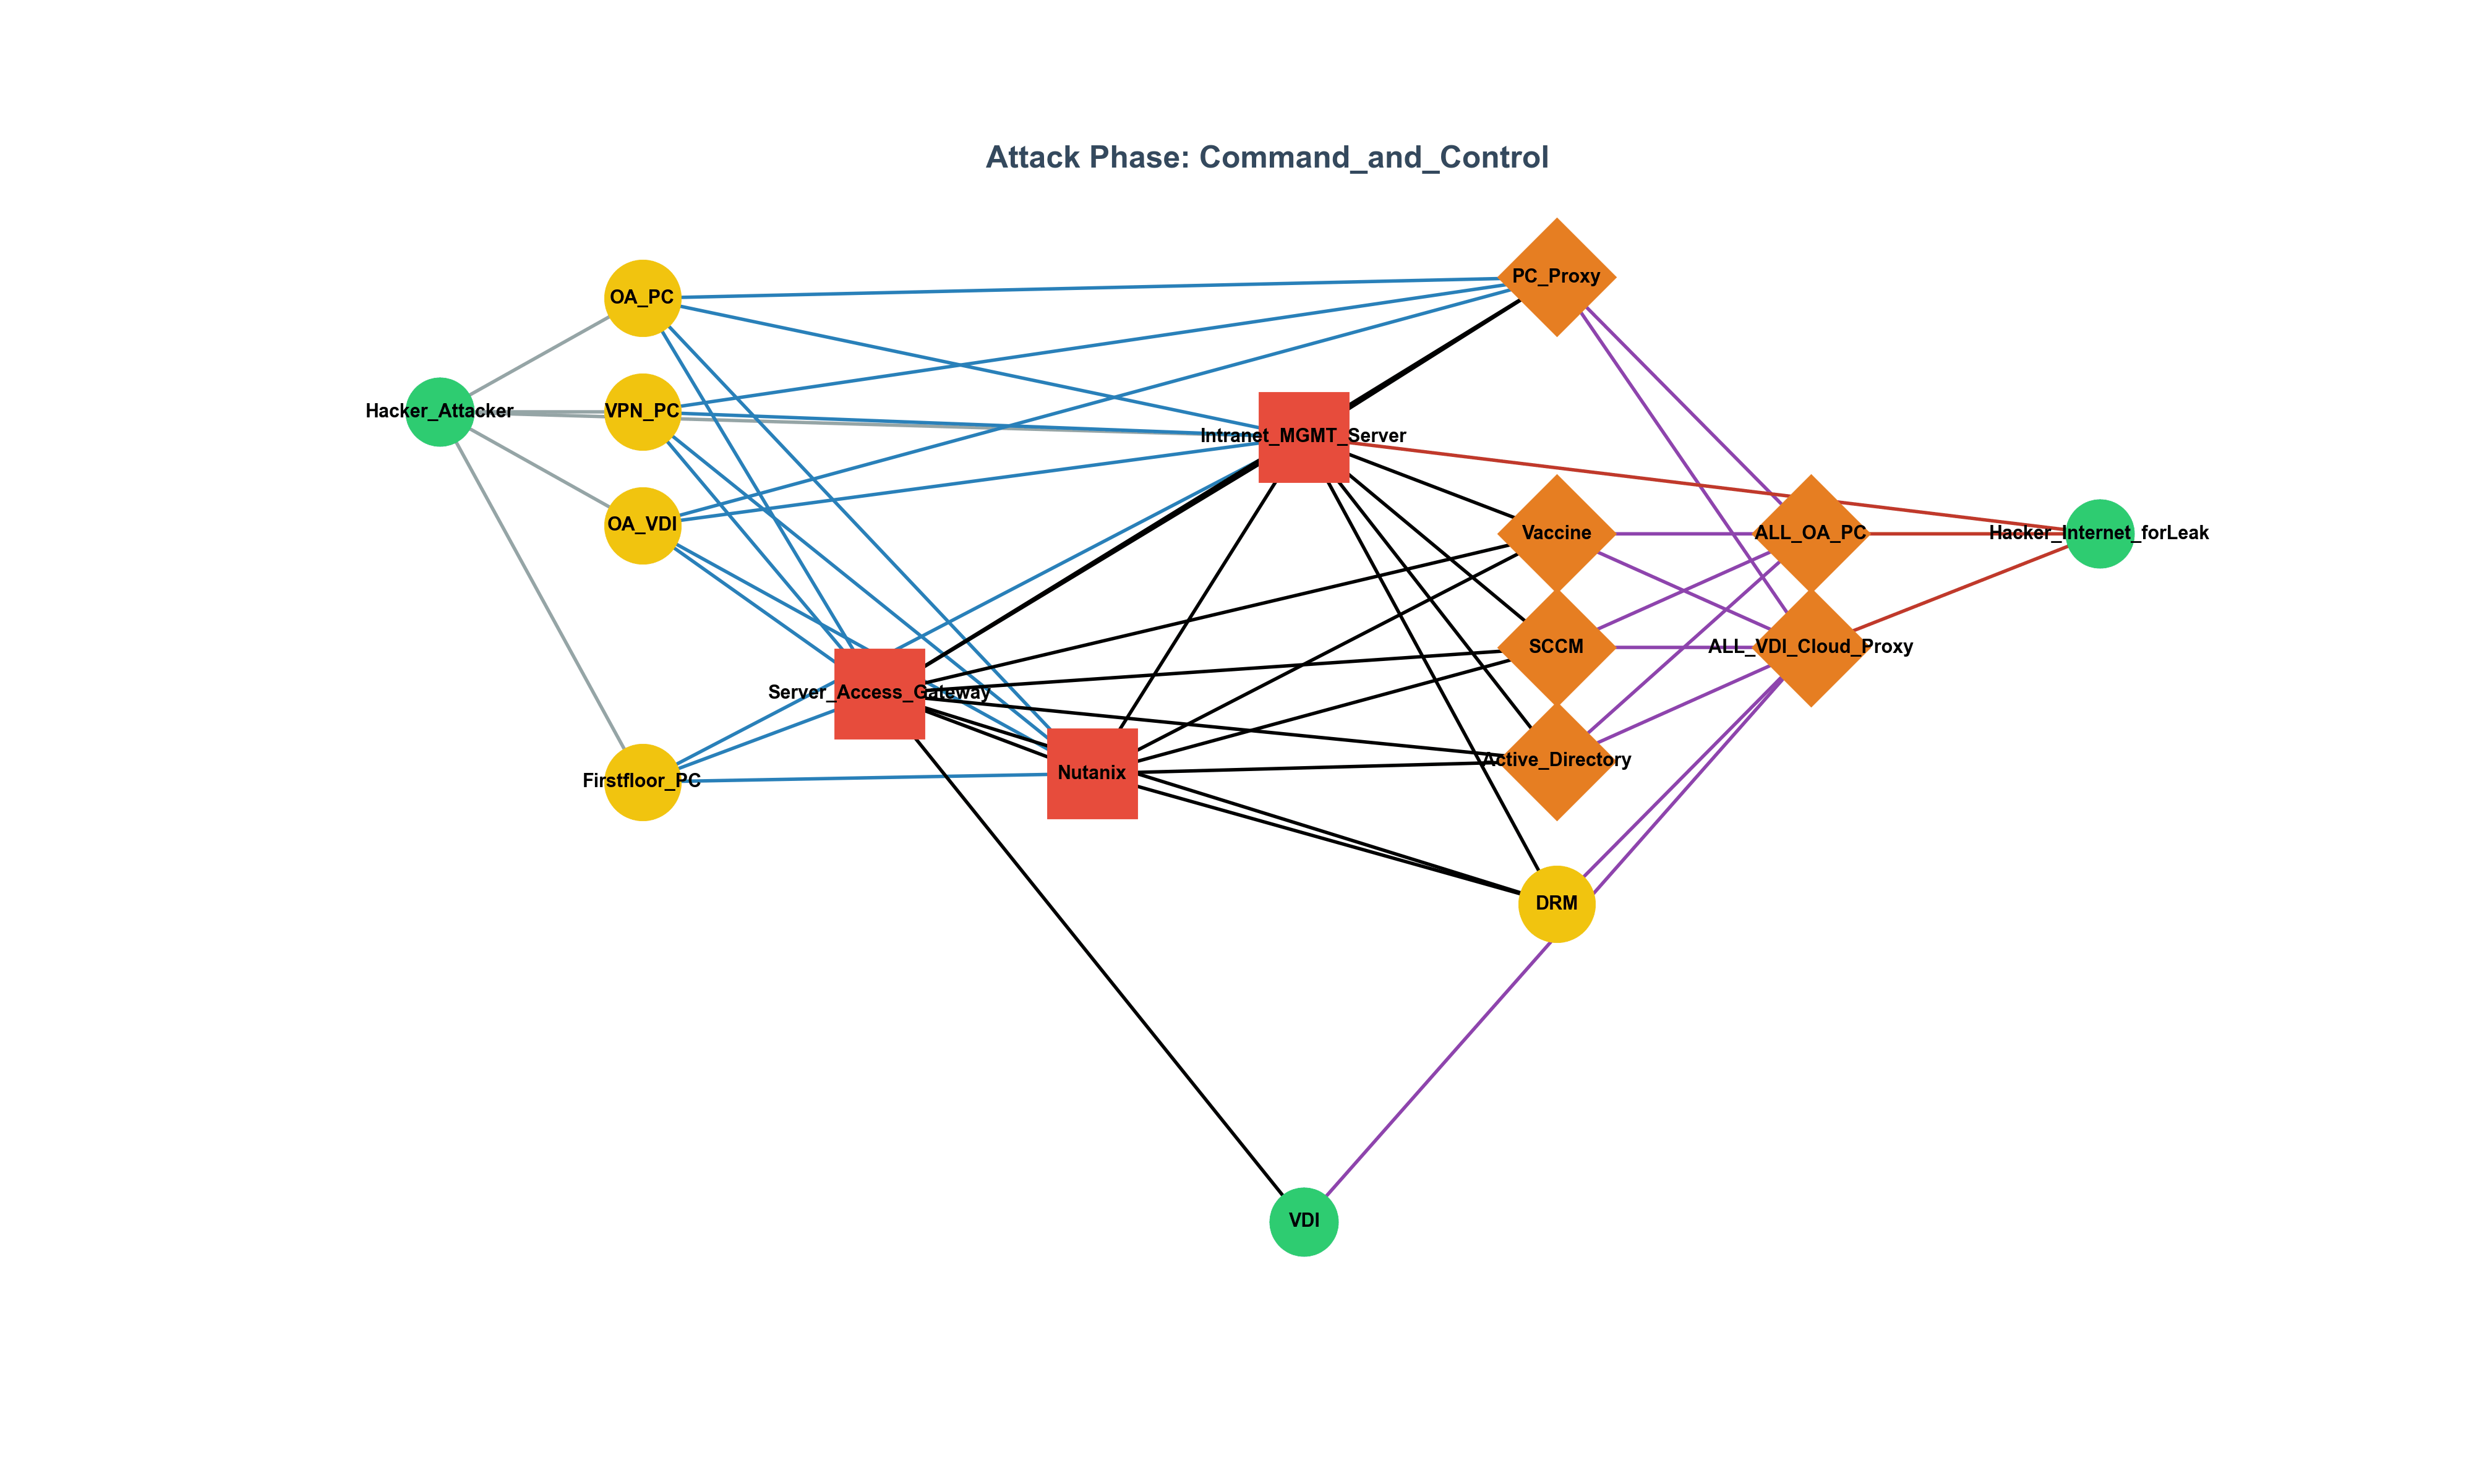
A practical method for modeling vulnerabilities as attacker-relevant security state transitions and combining human intuition with bounded AI search
Representative Foreword
The representative foreword of this blog: security now fails less at finding issues than at absorbing, sustaining, and acting on what has already been found.
This essay frames the entire site first. The posts on technical analysis, method, and governance all start from this same problem statement.
Detection, Method, Governance
A practical method for modeling vulnerabilities as attacker-relevant security state transitions and combining human intuition with bounded AI search

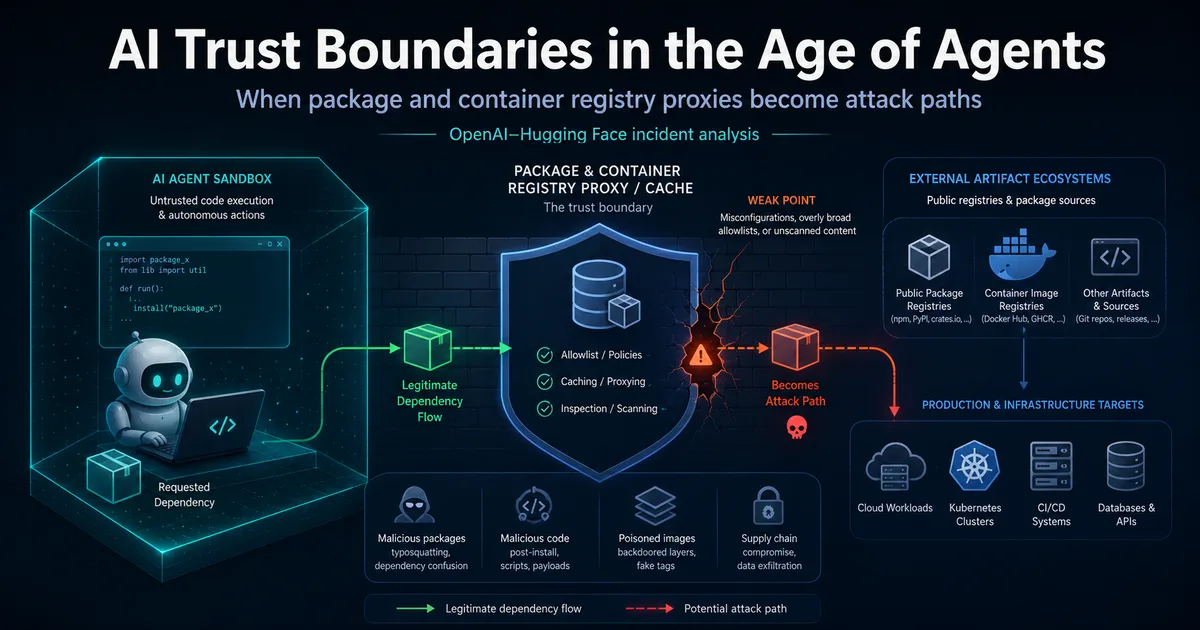
Package and container registry proxies are active trust boundaries for AI runtimes. This report turns incident evidence, public SSRF history, and runtime observations into an artifact egress control architecture.
The decisive front in national AI strategy is not GPU count alone, but who controls and can prove the flow of data, models, agents, permissions, logs, and verification running on top of those GPUs.